Oct 17 2026

SFO “elected” to pay for DHS facial recognition system
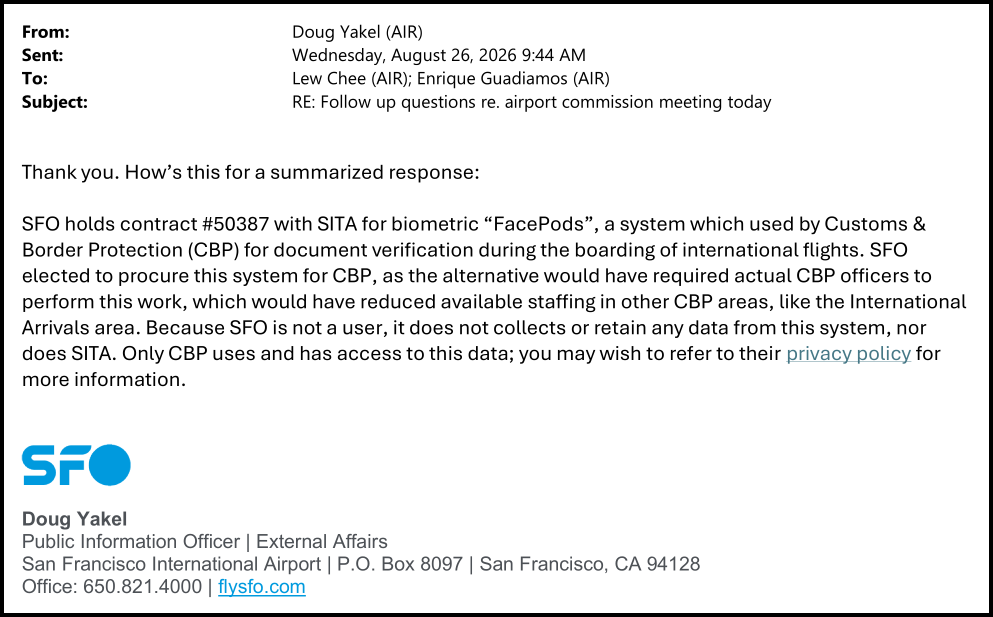
[Internal SFO email message released in response to our public records request. The claim that only CBP has access to the facial images is false. The official CBP notice for these records indicates that they are routinely shared with other DHS components, which include ICE, and with other US and foreign agencies.]

We’ll be back at the San Francisco Airport Commission on Tuesday, October 20th (9 a.m., S.F. City Hall, Room 400) to renew our demands for the airport to end its illegal funding of facial recognition infrastructure for immigration enforcement, review and publicly report on all of its contracts and collaboration with the US Department of Homeland Security (DHS), and post prominent signs warning travelers of the invisible risk that information in airline reservations, even for domestic flights, can be passed on to Immigration and Customs Enforcement (ICE) and used to target travelers for detention or deportation.

The last scheduled Airport Commission meeting was canceled. We’ve received no response to any of our specific requests for action by the Airport Commission.  In the meantime, though, we’ve received responses to some of our requests for airport records which confirm the illegality of some of the airport’s actions and the need for action.

Internal SFO email messages show that SFO officials illegally “elected” to pay for facial recognition cameras connected to to the DHS Traveler Verification Service, in order to spare US Customs and Border Protection officers from having to photograph departing international passengers and free up CBP officers to spend more time on other duties at the airport — duties which include assisting ICE officers with detentions of travelers and other immigration enforcement activities.

According to one internal SFO message summarizing information provided by airport operations managers:

SFO holds contract #50387 with SITA for biometric “FacePods”, a system which used by Customs & Border Protection (CBP) for document verification during the boarding of international flights. SFO elected to procure this system for CBP, as the alternative would have required actual CBP officers to perform this work, which would have reduced available staffing in other CBP areas.

Facial images taken by these city-funded cameras are transmitted over a city-funded connection to CBP. CBP shares them with other DHS components including ICE, and uses them to train the facial recognition algorithm used by ICE to determine who to detain or deport.

When this system was first tested, CBP officers staffed the cameras. But CBP has since tried to get airports to provide the cameras and and airlines to operate them. Airlines are incentivized to collaborate in this passenger surveillance and control scheme by being given free use of the TVS system (paid for, in this case, by SFO) for their own business process automation and commercial surveillance.

Pursuant to San Francisco’s Sanctuary City Ordinance, city and county agencies such as the airport may not “elect” (i.e choose) to provide or pay for services to support immigration enforcement. City funds may be spent on such services not as a voluntary choice but only to the extent required by Federal regulations.

Federal regulations (8 CFR §234.4) require each international airport to pay for some services and facilities for use by Federal immigration enforcement agencies, including “such temporary detention quarters as may be found necessary.”

SFO Airport Director Mike Nakornkhet and S.F. City Attorney David Chiu wrote to CBP earlier this month  to “express concern” about CBP’s treatment of detainees at SFO. But this focuses attention on precisely that aspect of immigration enforcement at SFO over which the city has the least control. This makes it easy for city officials to claim that their hands are tied — as they are, to some degree, with respect to the immigration jail at SFO.

But not everything Federal agencies ask the airport to provide is required by Federal regulations. The Airport Director, the City Attorney, and the Airport Commission should focus on the decisions within their control: voluntary financial support by SFO for facial recognition  infrastructure and services used for immigration enforcement, and signage to warn travelers about the invisible risks of airline-TSA-ICE data sharing.

No Federal regulation requires any airport to provide, or any airline to use, the TVS facial recognition system. The notice of CBP’s regulations for use of facial recognition for departing air travelers makes explicit that, “Participation in CBP’s biometric entry-exit program will remain voluntary for carriers under this final rule. If air carriers or airports do not participate, they will continue conducting manual identity verification.”

TVS is a choice for the airport — a choice that the Sanctuary City Ordinance prohibits SFO to make. Voluntary funding of immigration enforcement activities by any agency of the City and County of San Francisco, including the airport, is forbidden.

SFO’s contract #50387 with SITA is a voluntary payment for services that are used for immigration enforcement. As such, it is prohibited by the S.F. Sanctuary City Ordinance. It is the legal duty of the S.F. Airport Commission to terminate this contract immediately. We reiterate our demand that the Airport Commission place the termination of contract #50387 on its agenda for action at its next meeting.
Read More →

Aug 30 2026

SFO evades criticism of its role in immigration enforcement

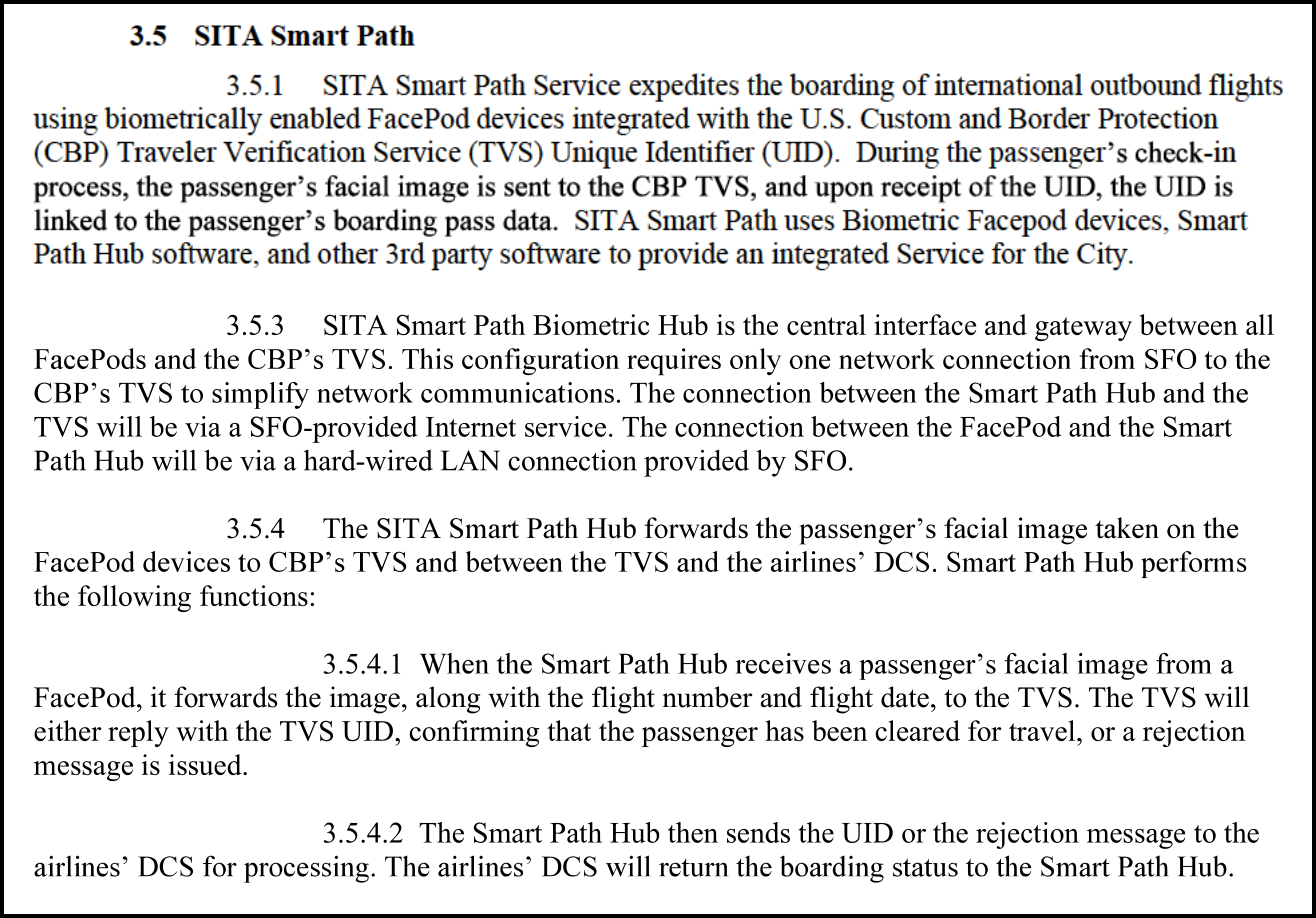
[Excerpt from illegal contract awarded by SFO to SITA in violation of the S.F. Sanctuary City Ordinance describes facial recognition hardware, software, and services paid for by the City and County of San Francisco, deployed by SITA on City and County property at SFO, and used to collect and transit mug shots of passengers and “permission to board” messages between airlines, the airport, and CBP/DHS, for purposes including immigration enforcement.]

At the San Francisco Airport Commission meeting on August 15th, a dozen members of the public (video, Mission Local, SF Public Press) called on the Airport Commission to comply with San Francisco’s “Sanctuary City” ordinance, which prohibits use of S.F. City and County resources — including airport property and funds — for immigration enforcement.

Another 35 people sent written comments to the Airport Commission on the same subject.

Many of the commenters, who included including supporters of Indivisible SF, Bay Resistance, and the Identity Project, among others, explicitly endorsed the comments of the Identity Project and our specific requests for action by the Airport Commission.

The Airport Commissioners neither discussed nor responded to any of our criticism. But the Director of SFO, Mike Nakornket, opened the meeting by trying to preemptively deflect our criticism with a mix of false, untested, inadequate, and unresponsive claims about the city’s actions and legal authority as the owner, landlord, and operator of the airport.

False: Airport Director Nakornket  claimed that, “SFO is not involved in the sharing of passenger information for immigration enforcement  purposes, which we understand occurs on a federal level between DHS agencies.”

But the Airport Director should know that this isn’t true.

Read More →

Feb 05 2026

CBP keeps its app for US visitors secret

Should a visitor to the US have to install and use a US government app that runs secret code to collect an unknown amount of data using any or all of their phone’s sensors, connects to other unknown data sources and recipients, and uses secret algorithms based on that secret dataset to “auto-deny” some ESTA applications to visit the USA?

We say no — and so does US law.

In December 2025, US Customs and Border Protection (CBP) announced that it planned to shift the Electronic System for Travel Authorization (ESTA) from a website to an app, greatly expand the range of data collected from ESTA applicants, and delegate authority to the app to “auto-deny” some applications.

CBP proposed no rules to govern the proposed “auto-denial” of ESTA applications. We can find no basis in any law for such an automated decision-making procedure. But CBP gave notice that it intends to seek approval for this new and revised app-based collection of ESTA information from the Office of Management and Budget (OMB).

According to the Paperwork Reduction Act (PRA), the request for OMB approval must be preceded by notice of the proposed collection of information, followed by a window of at least 60 days for members of the public to review and submit comments on the proposal.

PRA regulations at 5 CFR §1320.8(d)(2) require that this notice include a complete copy of the proposed collection of information or instructions on how any member of the public can obtain a copy, free of charge, and still have 60 days to review and comment on the proposal.

But CBP didn’t include a copy of the code or any other part of the ESTA app in any format in its notice in the Federal Register. As the 60-day notice-and-comment window runs out, CBP  still has not responded to our repeated requests for this information.

As we note in the comments we filed with CBP:

Since the day this notice was published in the Federal Register we have been diligently, but to date entirely unsuccessfully, attempting to request and obtain a copy of the proposed collection of information from the points of contacts specified in the notice.

This isn’t just a procedural error. The failure to provide valid notice denies us and all other members of the public the opportunity to provide informed comment on the ESTA app, which would require an expert review and audit of the source code.

As of now, we’ve seen none of the user interface screens of the proposed ESTA app; none of the PRA, Privacy Act, administrative appeal rights and procedures, and/or other notices (if any) provided to users of the app; none of the code specifying what data is collected, transmitted, and received by the app;  and none of the code embodying the algorithms and specifying the data they use as the basis for “auto-denial” of some ESTA applications.

The proposal for collection of more information and robo-adjudication of the equivalent of visa applications would be a bad idea even if PRA procedures were followed. We’ll have much more to say about these proposals if and when CBP provides us with proper notice and a chance to inspect the workings of the proposed new version of the ESTA app.

If you’re an Android and/or iOS app developer who might be willing to volunteer your expertise to help us analyze and audit the workings of the ESTA app, if CBP ever publicly discloses its code, please get in touch.

But as of now, because the  notice was plainly invalid, OMB can’t legally approve the CBP proposal.

CBP must either withdraw or abandon this proposal or provide a valid new notice, with a complete copy of the ESTA app including its source code, followed by a new 60-day comment period. If CBP submits this proposal to OMB without first doing this, OMB must reject it as being in clear violation of the PRA regulations.

CBP isn’t using the standard Regulations.gov system for submission of comments on this proposal. If you want to submit your own comments, send them by email by to CBP_PRA@cbp.dhs.gov by midnight EST Monday, February 9, 2026. Be sure to include “Comments to CBP re: OMB Control Number 1651–0111” in the subject line of your email message.

Jan 02 2026

Collection of biometrics from anyone “associated” with a foreigner

As part of an array of proposals and rules issued by components of the US Department of Homeland Security to collect a widening array of biometric information and systems from widening categories of individuals, US Citizenship and Immigration Services  (USCIS) is proposing a new rule that would authorize collection of any form of biometric information or samples from anyone, including US citizens, “encountered” by USCIS or “associated with” any applicant for admission to the US, US residency, or US citizenship.

The proposed rule would give USCIS blanket authority, at its discretion, to order any such individual to report to any location worldwide specified by USCIS, and to submit to collection of facial images (“digital image, specifically for facial recognition”), fingerprints, palm prints, iris scans, retinal scans, voice prints, and/or DNA samples.

Underlying the proposal is an implicit but impermissible assumption that merely to “associate” with foreigners is sufficiently suspicious to create probable cause for a search.

Today the Identity Project and Fiat Fiendum, Inc., filed comments objecting to this proposal for warrantless, suspicionless searches as unconstitutional and contrary to US treaty obligations pursuant to the International Covenant on Civil and Political Rights:

U.S. Citizenship and Immigration Services (USCIS) component of the Department of Homeland Security (DHS) is proposing to “expand its routine biometric collections to include individuals associated with immigration benefit requests or other requests or require[d] collection of information…. DHS is proposing to revise 8 CFR 103.16 to require that any applicant, petitioner, sponsor, beneficiary, or individual filing or associated with a benefit request, other request, or collection of information, to include U.S. citizens, U.S. nationals, and lawful permanent residents, and without regard to age, must submit biometrics, unless DHS otherwise exempts the requirement.”

These individuals would be required to submit to intrusive searches at U.S. borders and ports of entry and exit, at places outside the U.S., and at places in the interior of the U.S.

These searches and collections of biometric information and samples would include facial photography (“mug shots”), fingerprinting, iris and retina scans, voice samples, and DNA samples, on a dragnet basis for all applicants or “associates” of applicants or at the “discretion” of USCIS, rather than on the basis of warrants, probable cause, or individualized suspicion.

The NPRM does not mention the Constitutional rights or human rights treaties it implicates, much less justify the proposed rules as Constitutional or permitted by treaty.

The proposed searches would be unconstitutional and violate U.S. treaty obligations.

Warrantless, suspicionless searches, solely on the basis of citizenship, immigration status, exercise of the right to freedom of movement, and/or “association” with other individuals, would violate the First and Fourth Amendments to the U.S. Constitution and U.S. obligations as a party to the International Covenant on Civil and Political Rights (ICCPR).

The proposed rule should be withdrawn.

Thousands of comments, almost all objecting to the proposed rule, are still being docketed. Once they are docketed, you can find all of the comments on this proposal here.


Dec 10 2025

CBP wants all visitors to install and use its smartphone app

Permisisons requeste by ESTA Android app

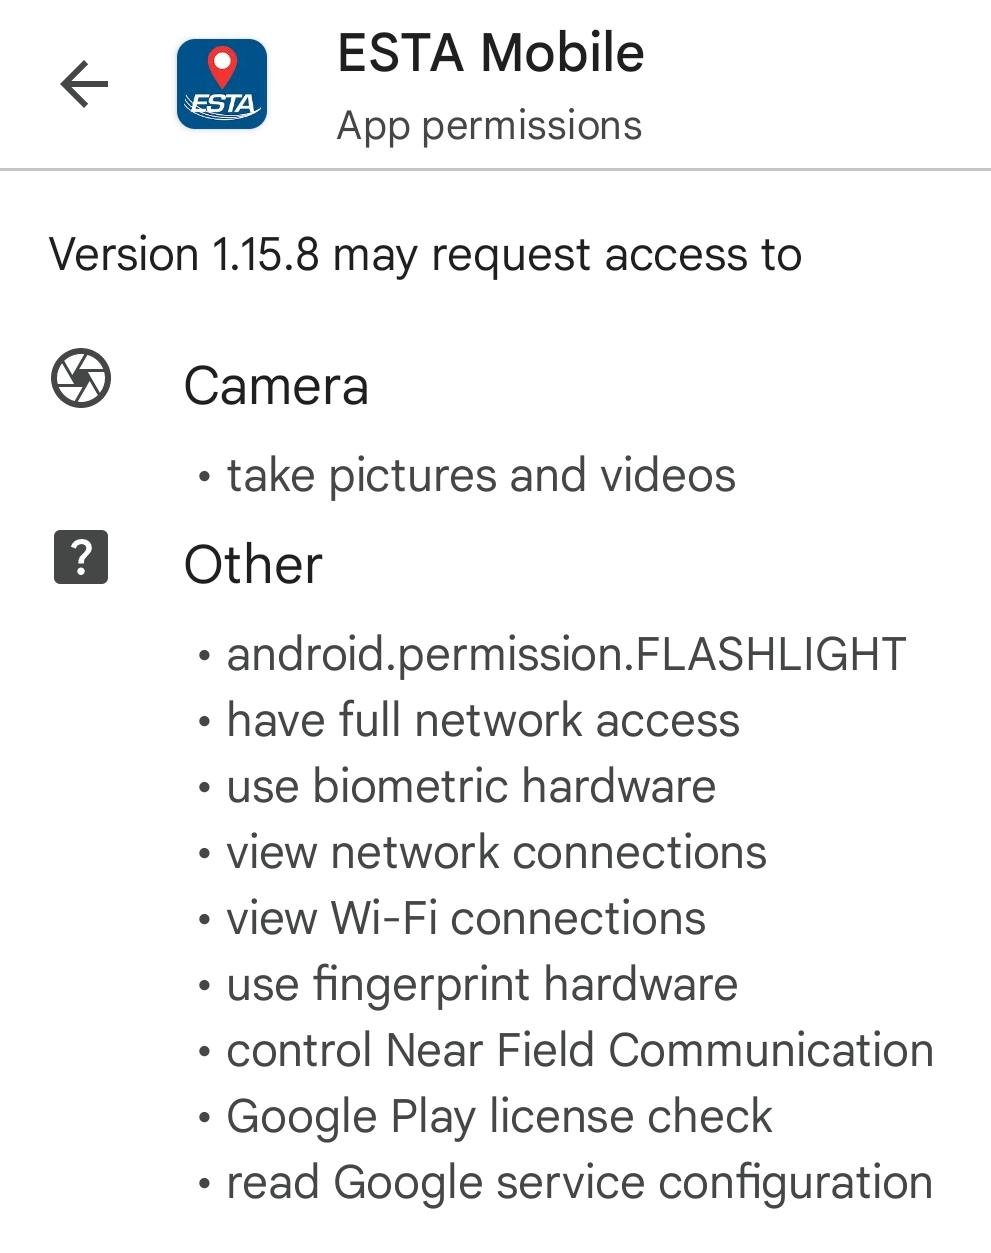
[Permissions requested by ESTA Android app. Why does CBP want to be able control your flashlight?]

By a notice published today in the Federal Register, US Customs and Border Protection (CBP) is requesting approval not only to make all foreigners visiting the US without visas submit a comprehensive set of biometric identifiers (“face, fingerprint, DNA, and iris”) but to do so by installing and using a closed-source CBP smartphone app that requires permission to access Wi-Fi scanning and network data; take photos and video; access any fingerprint, iris scan, or other biometric sensors, and even turn on and off your flashlight.

Each visitor to the US under the Visa Waiver Program (VWP), for which the fee has recently been raised from $21 to $40 per person, would be required to submit, in advance, through this smartphone app, identifiers for all social media accounts they have used in the last five years.

Each visitor would also be required to submit what CBP calls “High Value Data Elements”. According to the notice:

The high value data fields include:

a. Telephone numbers used in the last five years;
b. Email addresses used in the last ten years;
c. IP addresses and metadata from electronically submitted photos;
d. Family member names (parents, spouse, siblings, children);
e. Family number telephone numbers used in the last five years;
f. Family member dates of birth;
g. Family member places of birth;
h. Family member residencies;
i. Biometrics—face, fingerprint, DNA, and iris;
j. Business telephone numbers used in the last five years;
k. Business email addresses used in the last ten years.

CBP thinks that the average visitor could compile and enter all of this data (typing on a smartphone) in 22 minutes,  including the time needed to contact each of their siblings and children to find out their five-year history of addresses and phone numbers.

Welcome to the 2026 World Cup!

Applicants for US visas are already required to provide a much more extensive set of personal data, including biometrics and identifiers for all social media accounts they have used. So this proposal, if approved, would expand collection of biometrics, social media identifiers, and the additional “high value data elements” to almost all foreign visitors to the US, with or without visas. The only remaining exception, which CBP doesn’t mention, is for asylum seekers who may have no documents and who require no pre-approval.

We continue to oppose warrantlesss, suspicionless compelled disclosure of social media or biometric identifiers or other information as unconstitutional and a violation of the human rights of travelers. And we oppose any requirement to provide this information in advance, when it could be collected on arrival in the US, when visitors apply for admission.

Read More →

Nov 26 2025

CBP finalizes rule for mug shots of all foreigners entering or leaving the US

Last month US Customs and Border Protection (CBP) issued a final rule on Collection of Biometric Data From Aliens Upon Entry to and Departure From the United States.

If this new rule is Constitutional and otherwise valid, which we don’t think it is, it requires all non-US citizens entering or leaving the US to submit to mug shots. These will be used for a wide range of purposes in conjunction with automated facial recognition systems. Photography and automated facial recognition of all foreigners entering and leaving the US will be expanded from airports to all land border crossings.

This warrantless traveler surveillance and tracking program would cost more than $100 million per year, in CBP’s estimate (which explicitly puts zero value on privacy).

CBP proposed this rule in 2020, and we submitted comments (together with Restore the Fourth, Privacy Times, and the National Workrights Institute)  objecting to the proposal as procedurally improper — before even needing to reach the Constitutional issues it presented — and in violation of the Privacy Act and the Paperwork Reduction Act.

CBP says that, “After review of the comments, through this final rule, DHS is finalizing the proposed changes in the NPRM without substantive modification.” But CBP hasn’t cured the defects in the proposal, and brushed off our objections on the basis of patently false factual claims that can be disproved by even cursory review of CBP’s own website or the situation at any of the airports where travelers are being forced to submit to mug shots.

Along with its final rule, CBP announced another 30-day window for public comments, which closes today. But CBP only wants input on how to carry out this warrantless and surveillance and traveler-tracking program, not whether it is legal:

Comments submitted regarding any topic other than the specific collection process and costs and benefits on these newly implemented transportation modalities are out of scope for this final rule and will not be considered.

We have declined the opportunity to submit further comments on the “specific collection process” to be used by CBP for these unlawful warrantless searches. We’re not going to advise CBP on how to break the law. The rule is unlawful. If CBP is uninterested in comments on the validity of the rule, it can and should be challenged in court.

In response to our objection that CBP’s outsourcing of traveler surveillance to airlines and airports violates the Privacy Act, CBP said that:

DHS acknowledges that the Privacy Act requires that ‘‘each agency that maintains a system of records shall . . . collect information to the greatest extent practicable directly from the subject.’’ 5 U.S.C. 552a(e)(2) … Nevertheless, as explained in the NPRM, CBP considered and piloted many types of biometrics collections. Using information gleaned from the pilots as well as public feedback, CBP has concluded that partnering with carriers and airports to capture facial images is the most viable large-scale solution as it is highly effective, cost effective, and less disruptive than other possible methods.

It’s unclear what CBP means by “most viable”, but this response doesn’t satisfy the law. Whether outsourcing to airlines and airports is “cost-effective” or “less disruptive” is irrelevant to whether it is meets the far higher standard in the law that the government must “collect information to the greatest extent practicable directly from the subject”.

Maintaining a system of records about individuals in violation of the Privacy Act is potentially a criminal violation of the Privacy Act, although we won’t hold our breath for Federal prosecutors to seek indictments of Federal officials for such crimes.

In our comments, we also pointed out that the Paperwork Reduction Act requires CBP, like all other Federal agencies collecting information from the public, to provide individuals with specific notices including the consequences, if any, for not providing the information, and the OMB control number for the collection of information.

In response, CBP falsely claims that, “CBP displays the OMB control number on signage.”  The final rule that includes this false claim even cites the CBP website that includes model signs and notices— none of which include any PRA notice or OMB control number.

It’s unclear whether the CBP staff and officials who prepared and signed off on the final rule never actually looked at their own website or signage, or whether they were knowingly lying about their signage and notices.

Regardless of the reasons for the absence of proper signage, the PRA (44 U.S.C. §3512) creates an absolute defense for anyone — regardless of citizenship — against any  penalty for not providing requested information, including not submitting to airport mug shots, in the absence of a valid PRA notice at the point of collection of information, including a valid OMB control number applicable to the specific collection of information.

“Furthermore”, the final rule claims, “CBP regularly conducts periodic signage audits that include local CBP personnel to ensure signs are accurate and placed appropriately.”

We’ve seen no signs in any airport that include the required PRA notice or the OMB control number (1651–0138) which CBP claims apply to traveler mug shots. Any diligent, competent audit would have spotted this. Was CBP lying outright, and there were no audits at all? Or were any audits conducted with a lack of competence and/or diligence?

Regardless of whether the CBP staff and officials knew the claims in final rule were false, didn’t care if they were true or false, or simply didn’t bother to fact-check what they were signing off on, a rule justified by such patently false claims — indicative of bad faith, incompetence, and or gross negligence — fits the definition of a rule that is subject to challenge in court, pursuant to the Administrative Procedure Act, as “arbitrary, capricious, an abuse of discretion, or… unsupported by substantial evidence.”

CBP may not be interested in any further comments from the public about the legality of warrantless mug shots of travelers at airports an borders. But its actions remain subject to challenge in court under multiple Federal statutes as well as the Constitution.

Aug 01 2025

Senate postpones hearing on TSA facial recognition and ID verification

Earlier this week the Senate Committee on Commerce, Science, and Transportation postponed  a scheduled hearing on a bill that would limit some uses of facial recognition by the  Transportation Security Administration (TSA), while authorizing the TSA to carry out “identity verification” of airline passengers and take mug shots of all those air travelers who don’t show an “approved identification document”.

The original version of the “Traveler Privacy Protection Act” as it was introduced in 2023 would have imposed a straightforward prohibition on use of facial recognition by the Transportation Security Administration (TSA) without explicit Congressional authorization: “The Administrator [of the TSA] may not, for any purpose, use facial recognition technology or facial matching software in any airport unless such use is expressly authorized by an Act of Congress enacted after the date of the enactment of this Act.”

It is, of course, a sign of how far beyond its legal authority the TSA has already gone that Congress would need to consider a bill to explicitly prohibit the TSA from exceeding the authority it has been granted by Congress. But that’s the situation we’re in.

The revised version of the bill put forward in 2024 as an amendment to the Federal Aviation Administration reauthorization act and reintroduced as a standalone bill in 2025 would authorize use of facial recognition by the TSA for “confirmation of the identity of a passenger before admittance to the sterile area of the airport,” provided travelers are given notice that being photographed is voluntary and that the TSA “does not subject passengers who choose the opt-out option to discriminatory treatment, additional screening requirements, less favorable screening conditions, or other unfavorable treatment.”

The revised bill would also mandate that the TSA, “for each passenger who chooses the opt-out option, performs identity verification using an approved identification document and without collecting any biometric information from such passenger… The [opt-out] option … does not apply with respect to a passenger— (i) who does not provide an acceptable form of identification at a security checkpoint; and (ii) whose identity the Administrator may need to verify through alternative measures to enter the sterile area.”

This bill would thus impose a new obligation on the TSA to carry out “identity verification”, leaving it ambiguous what (if anything) is required of travelers. But as we noted when this revised language was first introduced last year, despite the ambiguity in the bill,  it would for the first time create at least an arguable statutory basis for the TSA to claim — as it undoubtedly would claim, in a shift from its consistent admission to date in court that no law or regulation requires air travelers to show any ID — that airline passengers are required to identify themselves in some fashion, either through an approved ID document or facial recognition.

Read More →

Mar 03 2025

Treasury Department says it won’t enforce ID requirement for corporate principals

The US Department of the Treasury has announced that it plans not to enforce the provisions of the Corporate Transparency Act (CTA) that were to go into effect next month requiring owners and principals of all corporations to file copies of government-issued ID credentials, including photos, with the Financial Crimes Enforcement Network (FinCEN).

The Treasury Department also says it plans to propose revisions to the CTA regulations that would limit the ID-filing requirement to principals of “foreign reporting companies”, a term that doesn’t appear in the statute and isn’t defined in the announcement.

We don’t want the government to try to enforce the CTA reporting requirement. But if the law isn’t going to be enforced, it should be repealed, not left on the books as a Sword of Damocles available to prosecutors to threaten or persecute disfavored businesspeople. And the proposed regulations, redefining which entities must file CTA reports, would appear to be contrary to the explicit language of the CTA statute as to who must file.

Press releases like this one form the Treasury Department aren’t binding on Federal prosecutors, even now, much less in the future. Regardless of this announcement, nobody subject to the CTA is safe from prosecution if they don’t file the reports required by the law.

There are few legal constraints on prosecutorial discretion. Many laws — including those that impose reporting and filing requirements — are routinely ignored and unenforced. Police and prosecutors, especially those with malign intentions, love to have laws like this on the books that everybody violates. That allows anyone to be prosecuted at any time, with the government claiming truthfully that it is merely “enforcing the law”. Only in rare cases is the government required to explain the real reasons why some people are prosecuted while others who are known to have violated the same laws are not.

To word it a little differently, the combination of unlimited prosecutorial discretion and universally violated laws is central to the phenomena of pretextual police action and pretextual prosecution. An essential part of the solution is the repeal of unenforced laws.

We welcome, in the short term, the nonenforcement of CTA reporting rules. And we urge Congress to address the problem, promptly, by repealing the CTA in its entirety.


Feb 25 2025

“TSA must go away”


Thanks to a mutual fan, we were invited to speak about the work of the Identity Project with Alex Newman on the latest edition of The Liberty Report on Patriot.tv and Rumble.

We talked about current and long-term concerns including digital ID, the REAL-ID Act, how demands for ID enable surveillance and control and are being increasingly integrated into a global system of surveillance and control of our movements, and the importance of anonymous cash payment for protection against financial surveillance.

What can be done? We talked about the need for popular vigilance and popular resistance, but also about what the government could do:

If the Department Of Government Efficiency (DOGE) is really concerned about identifying  unnecessary and ineffective government programs to cut, they could start with the TSA.

Members of Congress could do their part by reintroducing the Freedom To Travel Act and working to abolish the TSA.

Most importantly, though, we the people can continue to resist these attacks on our freedom.

Thnaks to Alex Newman and his crew for giving us a chance to bring these issues to his listeners and viewers.

Feb 24 2025

Supreme Court reinstates new requirement for IDs and mug shots of corporate principals

The US Supreme Court has stayed the nationwide injunction against enforcement of a Federal law requiring owners or principals of all corporations to submit copies of ID documents, including photos, to the  Financial Crimes Enforcement Network (FinCEN) of the US Department of the Treasury.

The Supreme Court’s ruling leaves business owners and officers, and FinCEN, scrambling to figure out what to do — at a moment when how the Federal government might use personal information in ways that weren’t anticipated when it was collected is a hot topic.

The original deadline for filing of Beneficial Owner InformatIon (BOI) with FINCEN was to be January 1, 2025. But by then, multiple lawsuits against the Corporate Transparency Act had been filed, and the judge in one of those caseS had issued a nationwide injunction against enforcement of the law while the lawsuits were pending.

The Supreme Court’s decision to overturn that injunction allows the lawsuits and appeals to continue, but in the meantime allows the government to enforce the filing requirement.

Following the stay of the District Court injunction pursuant to the Supreme Court’s decision, FinCEN announced a new deadline of March 21, 2025, for filing of BOI (including copies of IDs) for most companies. Another injunction from a different judge in a different Federal court district remains in effect, but it applies only to the plaIntiffs in that case.

FinCen estimates that collecting and submitting the required information will require, on average, 90 to 650 minutes per company. That’s a far from trvial burden for, for example, a  sole proprietor with a personal LLC. The cost could be much higher for even a small business thta has to hire a lawyer to figure out who is considered a “beneficial owner” or officer subject ton the reporting requirement.

Those who search for information on the Web about BOI filing requirments are likely to be led to the flood of scam sites set up to rip off would-be BOI filers with excessive facilitation fees as intermediaries, while harvesting personal information for identity theft.  What does it say about the purposrted justification for this rule that the requirements of the “Financial Crimes Enforcement Network” are providing a windfall for financial fraudsters?

The purported limitations and controls on access to and use of BOI filings ring hollow in light of the access to and use of personal information from Federal databases in unanticipated ways and by entities and by newly-created entities with ambiguous authority, such as the White House Department Of Government Efficiency (DOGE).

With concern growing about how this informaiton might be misused, legislation is pending in Congress to repeal the Corporate Transparency Act or postpone its effective date.

On February 10th, the House of Representatives approved H.R. 736, a bill to extend the BOI filing deadline until January 1, 2026, by a unanimous vote of 408 to 0. The same or a similar bill is likely to be introduced in the Senate. Postponement might give time for the pending appeals in the lawsuits challenging the law to play out, or for Congress to repeal the law.

A bill to repeal the Corporate Transparency Act and the BOI reporting requirement has been introduced in the House as H.R. 425 and in the Senate as  S. 100, “Repealing Big Brother Overreach Act”. No action has yet been taken on this bill in either chamber.