Sep 14 2026

Court bars AAMVA from giving away driver’s license data — for now

Last Thursday, September 10th, Judge Anthony Trenga of the U.S. District Court for the Eastern District of Virginia heard arguments on whether his temporary restraining order (TRO) barring the bulk transfer of commercial driver’s license records from the American Association of Motor Vehicle Administrators (AAMVA) to the U.S. Deopartment of Transportation (DOT) should be converted into a preliminary injunction.

If granted by the court, a preliminary injunction would remain in effect until a final ruling in the lawsuit brought by state governments challenging the data demand by the Feds.

Judge Trenga took the motion for a preliminary injunction under advisement without issuing a decision.

In response to the motion for a preliminary injunction, DOT cooked up an array of patently pretextual and impermissibly ex post facto new excuses for why it needs a dump of all the records of commercial driver’s licenses in AAMVA’s SPEXS database.

DOT also made a new threat to have its Office of Inspector General demand the data, in bulk, without a warrant or probable cause, for investigation of unspecified possible crimes.

It seems unlikely that either the briefs or the oral argument last Thursday have given Judge Trenga any reason to depart from the reasoning in his initial decision granting a TRO.

In that ruling, Judge Trenga found multiple independent ways in which the demand for this data is illegal. He also found that the claimed basis for the demand is a pretext to obtain data that would actually be used (illegally) for immigration enforcement:

The FMCSA has also conceded it has not demanded the MPRs [Master Pointer Records] solely to use those records itself, but also to share them with DHS for “immigration enforcement purpose[s].”… But the relied upon exception under the DPP A that authorizes disclosure of protected data to effectuate FMCSA’s own statutory mandate does not authorize FMCSA to simply pass that data onto another agency….

[W]hen repeatedly pressed at the hearing on this point, the Federal Defendants were unable to explain how the data would in fact assist them in performing their statutory functions, or point to anything that they cannot already do without this data…

Federal Defendants have failed to dispel the compelling inference that they seek these 17 million files in large part, if not primarily, for immigration enforcement, which is not part of [FMCSA]’s statutory mandate….

[B]ecause the Data Demand is unlawful, the public interest inherently favors issuing an injunction….

The issuance of an injunction is also in the public interest given the harm the termination of federal funding to AAMVA would cause since CDLIS would effectively cease its operations and impair Plaintiff States’ ability to issue and renew CDLs and compromise the safe operation of commercial motor vehicles…. Furthermore, as the AAMVA contends, the “CDLIS … is interconnected with all forms of driver licensing” and therefore any shutdown “could disrupt, or even stop, the issuance and renewal of any driver license in the United States.”

Meanwhile, the American Federation of Teachers (AFT) has moved to intervene in the case on behalf of AFT members including school bus drivers whose commercial driver’s license data is included in the Federal data demand.

AFT says that states — like AAMVA — have their own interests, including retaining Federal funding, and can’t be relied on to represent the interests of individuals whose data is at risk. AFT’s motion to join the case against both DOT and AAMVA is set for a hearing this Wednesday, September 16th.

While Judge Trenga has ordered AAMVA, for now, not to hand over records of all commercial driver’s licenses to DOT, the outcome of the lawsuit remain uncertain.

No one state such as California can control AAMVA’s decisions. The head of each state’s driver licensing agency has one vote on AAMVA’s board of directors, so states that want to hand over AAMVA’s records for immigration enforcement can outvote those that don’t.

The ongoing litigation should teach a lesson to California and other states that once they hand over data to AAMVA, they can’t control to whom or for what purposes it is passed on voluntarily or involuntarily by AAMVA to Federal agencies or other third parties.

The same lesson applies to non-commercial as to commercial driver’s licenses, both of which are stored by AAMVA in the same database. In  comments to Wendy Fry and Khari Johnson of Cal Matters, a spokesperson for California Governor Gavin Newsom falsely claimed that AAMVA’s databases of commercial and non-commercial driver’s license records “are separate systems”. In fact, CDLIS records for commercial driver’s licenses and S2S records for non-commercial licenses are both stored by AAMVA in the same SPEXS database.

Californians should have second thoughts about the upload of non-commercial driver’s license records to SPEXS, planned for 2027 and authorized by a law rushed through the state legislature by Governor Newsom while Federal demands for SPEXS data were already pending.
Sep 01 2026

9th Circuit upholds injunction against cash transaction reporting order

In March 2025 we reported on an order from the Financial Crimes Enforcement Network (FinCEN) of the US Department of the Treasury commanding all money transfer agencies and currency exchanges in seven counties in California and Texas along the US-Mexico border to file reports with FinCEN including the identities of all customers engaging in all cash transactions over $200.

Separate lawsuits challenging this order were brought by the Institute for Justice on behalf of storefront financial services business in California and Texas.

FinCen revised and reissued the order several times, raising the reporting threshold from $200 to $1000 and changing the areas to which the order applied. But despite these moves by FinCEN, US District Courts in both California and Texas issued preliminary injunctions against enforcement of the order.

A year later, a panel of the 9th Circuit Court of Appeals has upheld the injunction in the California case by a 2-1 vote.

Read More →

Aug 31 2026

Airline reservations are still being used to target dissidents

Much of the public interest in the case of Samuel Tunick has focused on the charge — carrying up to a five-tear prision sentence — that  Mr. Tunick “destroyed property to prevent its seizure” by the government by giving Customs and Border Patrol (CBP) agents at the Atlanta airport a “duress password” for a smartphone Mr. Tunich was carrying when he returned from an international trip.

The phone seized from Mr. Tunick at the airport was running Graphene OS, an open-source variant of the Android operating system. When one of the CBP agents entered the password Mr. Tunick (under duress) provided, it wiped the phone’s user memory and reset the phone to a state as though the OS had just been installed.

The option to set a “duress password” that wipes the phone, in addition to one or more user passwords for separate user spaces, is a feature of Graphene OS intended to reduce the risk of coerced disclosure of data.

Mr. Tunick was arrested at the airport last December, but briefing on pre-trial motions is ongoing and no trial date is in sight.

This is an important test case on the issues raised by the “duress password”, the way it functions in Graphene OS, and compelled disclosure of passwords generally.

But there’s another concerning issue raised by the facts in this case: How airline reservations were used to target Mr. Tunick, in advance, for special treatment on arrival including seizure of his phone and pressure to disclose a password for the phone.

Mr. Tunick wasn’t singled out for “secondary screening” at random or because of anything he said or did or was carrying that appeared “suspicious” to CBP agents at the airport.

According to a report of a motion hearing in July, the transcript of which has not yet been released, CBP agents were sent an automatically generated email message before his flight got to Atlanta, alerting them in advance that a person in whom they had previously indicated an interest had reservations on a specific airline, flight number, date, and time.

Read More →

Aug 30 2026

SFO evades criticism of its role in immigration enforcement

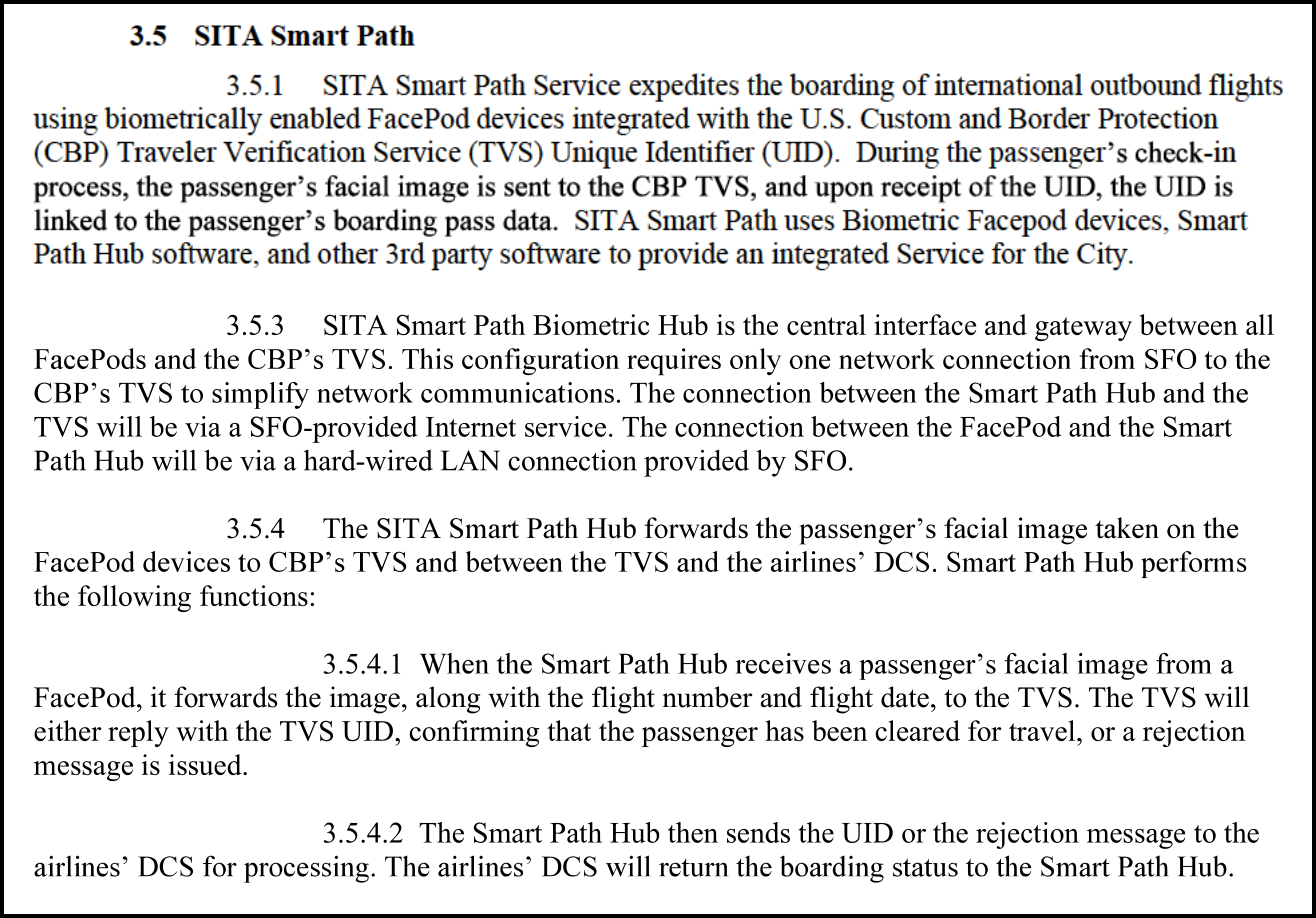
[Excerpt from illegal contract awarded by SFO to SITA in violation of the S.F. Sanctuary City Ordinance describes facial recognition hardware, software, and services paid for by the City and County of San Francisco, deployed by SITA on City and County property at SFO, and used to collect and transit mug shots of passengers and “permission to board” messages between airlines, the airport, and CBP/DHS, for purposes including immigration enforcement.]

At the San Francisco Airport Commission meeting on August 15th, a dozen members of the public (video, Mission Local, SF Public Press) called on the Airport Commission to comply with San Francisco’s “Sanctuary City” ordinance, which prohibits use of S.F. City and County resources — including airport property and funds — for immigration enforcement.

Another 35 people sent written comments to the Airport Commission on the same subject.

Many of the commenters, who included including supporters of Indivisible SF, Bay Resistance, and the Identity Project, among others, explicitly endorsed the comments of the Identity Project and our specific requests for action by the Airport Commission.

The Airport Commissioners neither discussed nor responded to any of our criticism. But the Director of SFO, Mike Nakornket, opened the meeting by trying to preemptively deflect our criticism with a mix of false, untested, inadequate, and unresponsive claims about the city’s actions and legal authority as the owner, landlord, and operator of the airport.

False: Airport Director Nakornket  claimed that, “SFO is not involved in the sharing of passenger information for immigration enforcement  purposes, which we understand occurs on a federal level between DHS agencies.”

But the Airport Director should know that this isn’t true.

Read More →

Aug 14 2026

DHS demands AAMVA’s national commercial driver database


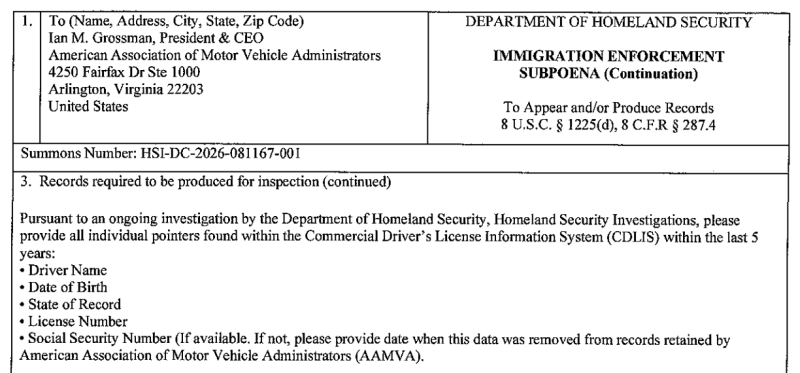
The US Department of Homeland Security (DHS) has subpoenaed the American Association of Motor Vehicle Administrators (AAMVA) for a copy of all entries in the CDLIS national database of state-issued commercial driver’s licenses held by AAMVA. The administrative subpoena was issued August 11th and ordered AAMVA to hand over a copy of all records that were found in the CDLIS database any time in the last five years, by 8 am Monday, August 17th.

DOT says that “AAMVA operates the CDLIS database on behalf of the federal government; it is contractually and legally obligated to furnish the requested records at FMCSA’s direction.”

In response, a group of states led by Illinois has filed separate lawsuits in Virginia, where AAMVA is incorporated, against the DHS to quash the subpoena and against AAMVA and the US Department of Transportation (DOT) to enjoin AAMVA from complying with the DOT’s parallel demand for the same data.

US District Judge Anthony Trenga immediately issued temporary stays which prohibit AAMVA from complying with the subpoena and prohibit any actions by DOT to punish AAMVA for noncompliance with the DHS subpoena or DOT demand for CDLIS data. Initial hearings before Judge Trenga in both cases are scheduled for Thursday, August 20th.

We hate to have to say, “We told you so.” But in this case, we told you so.

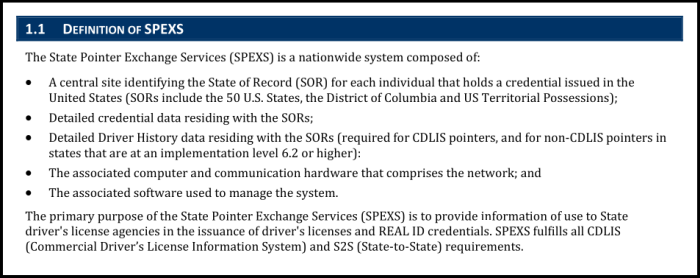
The CDLIS database is the little brother for commercial driver’s licenses (for truckers) to the big brother SPEXS database for all driver’s licenses and state-issued ID cards. Like SPEXS, CDLIS is a national database of “pointer” records (including name, date of birth, state, license or ID number, and Social Security Number)  aggregated from information uploaded by state motor vehicle agencies but held by AAMVA or AAMVA’s contractors.

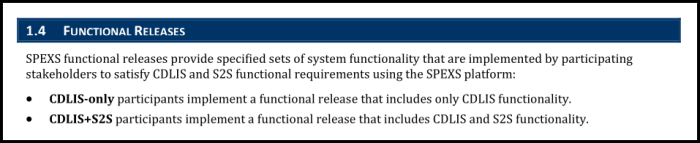
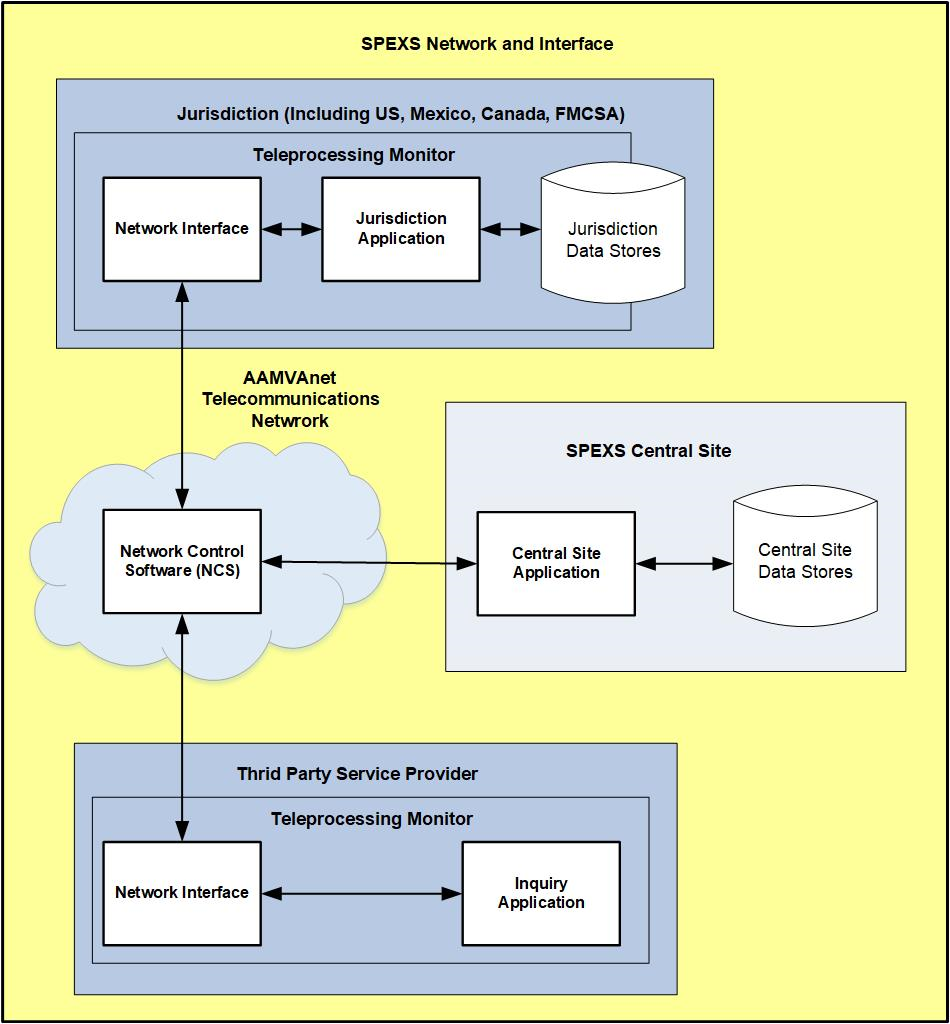
CDLIS (commercial license) and S2S (non-commercial license) pointer records are all stored in the same SPEXS database as part of AAMVA’s central site:

[Excerpts from AAMVA’s “SPEXS System Specification”]

We’ve warned repeatedly that once data is uploaded to AAMVA’s SPEXS database, Federal agencies could demand it from AAMVA in bulk. State authorities, most recently in California, have brushed off our warnings. But as conceded in declarations from the California Department of Motor Vehicles in one of the new cases, the California DMV has already been uploading CDLIS information about commercial driver’s licenses to SPEXS, and plans to start uploading “S2S” data about all California license to SPEXS in 2027.

The DHS is now seeking to obtain driver’s license data from every state, in bulk, through an administrative subpoena to AAMVA, for use for immigration enforcement, in exactly the manner and for the purpose we predicted and warned about.

AAMVA’s role is noteworthy and contemptible, although unsurprising.

AAMVA was sent a demand for the entirety of the CDLIS database on June 25th, but didn’t tell the states that had uploaded the data  in question about the Federal demand until almost a month later on July 23rd. State can’t count on prompt notice from AAMVA.

Even now, AAMVA isn’t  challenging the demand for CDLIS data. AAMVA is a defendant, along with the Federal agencies, in the lawsuits brought by states to protect their residents’ data against bulk disclosure to Federal agencies for immigration enforcement.

According to the complaints, the DHS and DOT have threatened to cut off all Federal funding for AAMVA, including funding for CDLIS itself (and presumably also SPEXS), if AAMVA doesn’t hand over the requested data. AAMVA depends on Federal funding, so it can’t afford to challenge Federal demands, making it in effect a captive proxy for the Feds despite being a nominally non-governmental private nonprofit corporation.

Presumably, the Feds will learn from AAMVA’s failure to challenge their demands for the data it holds. Next time, they’ll come back with a subpoena that includes a gag order prohibiting AAMVA from disclosing the subpoena to states that uploaded the data, so states will have no chance to file lawsuits like the ones filed this week.

The obvious next step after that would be a similar demand for SPEXS data about ordinary non-commercial licenses, probably as soon as California completes its planned bulk upload to SPEXS sometime early in 2027.

Officials in California and other states can no longer claim this isn’t possible.

State legislators need to act, now, to withdraw their states from SPEXS, before the DHS expands its data demands from the commercial licenses in CDLIS to all licenses in SPEXS.

Jul 31 2026

“Can SFO rein in the feds?”

As discussed in a feature article today by Clara-Sophia Daly on Mission Local, recent searches and arrests of passengers trying to board domestic flights at San Francisco International Airport (SFO) have prompted us to question what the airport has done, and what more it could and should do, to comply with city ordinances regulating use of surveillance technology and restricting collaboration with immigration enforcement.

The arrest of Iryna Gorb by ICE at SFO on July 22nd and the search of Nikolas De Bremaeker by the TSA (and/or by Covenant Aviation Security, the contractor that supplies most of the checkpoint staff at SFO) at SFO on June 10th, raise questions about (1) the technologies in use to flag passengers to components of the Department of Homeland Security (DHS) based on airline reservations, (2) whether equipment owned or operated by the airport is used to collect data passed on the DHS, (3) what, if any, limits are placed on warrantless access by DHS agents to airport premises, and (4) whether the policies of the airport, as put in place by the SF Airport Commission as an agency of the City and County, comply with city ordinances.

For both domestic and international flights, the DHS requires airlines to send information about all passengers and their itineraries to DHS components starting 72 hours before departure.  Reservation and itinerary information for international flights is sent to US Customs and Border Protection (CBP) and included in its Automated Targeting System (ATS). Information for domestic flights is sent to the Transportation Security Administration (TSA) through its Secure Flight system.

No airline is allowed to issue a boarding pass for either a domestic or international flight unless and until it receives an individualized, per-passenger, per-flight permission message from the TSA or CBP in the form of a “boarding pass printing result” (BPPR). The default in the absence of a favorable BPPR is not to allow them to fly. These fly/no-fly decisions are based on a black box of secret algorithms that incorporate list-based rules (blocklists) and other rules based on other known and unknown data.

Once such a data collection and  algorithmic control mechanism is in place, it’s easy to add lists or other rules to the algorithm or add recipients to the data stream.

What’s less well known is that the DHS doesn’t just use the information it gets from airlines to decide whether or not to allow you to fly. It can also use this information to generate “handling codes” instructing checkpoint staff to conduct special searches of your person and property, or to generate messages to other agencies that may want to arrange an “unwelcoming” party to intercept you at the airport, on departure or on arrival, to question, search, or arrest you – with or without a warrant.

We question the legality of many of these activities. Many of them have not yet been reviewed or approved by any court, and have little or no basis in law.

Airline passengers need to know that, legal or not, this is happening.

Travelers also need to know that, as we were the first to report last year (see here and here) and as was later confirmed by the New York Times and American Oversight, some of the most intrusive and legally questionable aspects of these systems of surveillance and control of air travel, based on reservation data from airlines, have in the last year been expanded from international flights to domestic flights. Air travelers should beware.

Read More →

Apr 01 2026

OMB gives blanket approval for USCIS social media surveillance

The White House Office of Management and Budget (OMB) has approved a request by US Citizenship and Immigration Services (USCIS) to require all individuals applying for or associated with applications for US visas, visa-free entry, residency, or citizenship to identify all social media accounts they have used in the last five years.

The new “generic clearance” approved by OMB spares USCIS from having to justify the purpose, relevance, and legality of demanding social media account information separately for each USCIS form or web page on which this information is demanded.

This approval by the current White House expands on the demand for social media identifiers first approved by OMB as one of the last actions of the Obama Administration.

Along with some other agencies, USCIS has adopted a new format for its analysis and response to comments on its regulatory proposals. The summary of comments appears to have been generated by an artificial intelligence chatbot. Unlike previous responses to comments that typically ignored or distorted many of the objections to agency proposals, the summary provided by USCIS to OMB is surprisingly accurate and complete. But rather than actually responding to the objections raised by the Identity Project and others, USCIS simply regurgitates a summary of its original claims about the proposal.

For example, in response to comments pointing out that collection of social media postings violates the Privacy Act’s prohibition on collection of information about acts protected by the First Amendment without explicit statutory authorization, USCIS merely repeats the conclusionary claim that, “Consistent with the requirements of the Privacy Act (5 U.S.C. § 552a(e)(7)), DHS does not maintain records ‘describing how any [citizen of the United States or alien lawfully admitted for permanent residence] exercises rights guaranteed by the First Amendment, unless expressly authorized by statute or by the individual about whom the record is maintained or unless pertinent to and within the scope of an authorized law enforcement activity.'” There’s no meaningful engagement with the comments or explanation of the basis for claiming that postings on social media aren’t protected by the First Amendment or that collecting this information is expressly authorized by any statute — which it isn’t.

The USCIS summary acknowledges our comments that social media surveillance violates US obligations pursuant to international human rights treaties. But in response, USCIS merely summarizes the statutes it claims implicitly authorize these actions — which of course says nothing about whether those statutes comport with US treaty obligations.

The response to comments also repeats the false and conclusionary claim that that, “Social media involves publicly available information that is accessible to anyone without a warrant”, even though in fact the identification of an individual with an anonymous or pseudonymous social media account isn’t otherwise accessible without a warrant.

We urge other countries not to follow this bad example of the US government.

Feb 05 2026

CBP keeps its app for US visitors secret

Should a visitor to the US have to install and use a US government app that runs secret code to collect an unknown amount of data using any or all of their phone’s sensors, connects to other unknown data sources and recipients, and uses secret algorithms based on that secret dataset to “auto-deny” some ESTA applications to visit the USA?

We say no — and so does US law.

In December 2025, US Customs and Border Protection (CBP) announced that it planned to shift the Electronic System for Travel Authorization (ESTA) from a website to an app, greatly expand the range of data collected from ESTA applicants, and delegate authority to the app to “auto-deny” some applications.

CBP proposed no rules to govern the proposed “auto-denial” of ESTA applications. We can find no basis in any law for such an automated decision-making procedure. But CBP gave notice that it intends to seek approval for this new and revised app-based collection of ESTA information from the Office of Management and Budget (OMB).

According to the Paperwork Reduction Act (PRA), the request for OMB approval must be preceded by notice of the proposed collection of information, followed by a window of at least 60 days for members of the public to review and submit comments on the proposal.

PRA regulations at 5 CFR §1320.8(d)(2) require that this notice include a complete copy of the proposed collection of information or instructions on how any member of the public can obtain a copy, free of charge, and still have 60 days to review and comment on the proposal.

But CBP didn’t include a copy of the code or any other part of the ESTA app in any format in its notice in the Federal Register. As the 60-day notice-and-comment window runs out, CBP  still has not responded to our repeated requests for this information.

As we note in the comments we filed with CBP:

Since the day this notice was published in the Federal Register we have been diligently, but to date entirely unsuccessfully, attempting to request and obtain a copy of the proposed collection of information from the points of contacts specified in the notice.

This isn’t just a procedural error. The failure to provide valid notice denies us and all other members of the public the opportunity to provide informed comment on the ESTA app, which would require an expert review and audit of the source code.

As of now, we’ve seen none of the user interface screens of the proposed ESTA app; none of the PRA, Privacy Act, administrative appeal rights and procedures, and/or other notices (if any) provided to users of the app; none of the code specifying what data is collected, transmitted, and received by the app;  and none of the code embodying the algorithms and specifying the data they use as the basis for “auto-denial” of some ESTA applications.

The proposal for collection of more information and robo-adjudication of the equivalent of visa applications would be a bad idea even if PRA procedures were followed. We’ll have much more to say about these proposals if and when CBP provides us with proper notice and a chance to inspect the workings of the proposed new version of the ESTA app.

If you’re an Android and/or iOS app developer who might be willing to volunteer your expertise to help us analyze and audit the workings of the ESTA app, if CBP ever publicly discloses its code, please get in touch.

But as of now, because the  notice was plainly invalid, OMB can’t legally approve the CBP proposal.

CBP must either withdraw or abandon this proposal or provide a valid new notice, with a complete copy of the ESTA app including its source code, followed by a new 60-day comment period. If CBP submits this proposal to OMB without first doing this, OMB must reject it as being in clear violation of the PRA regulations.

CBP isn’t using the standard Regulations.gov system for submission of comments on this proposal. If you want to submit your own comments, send them by email by to CBP_PRA@cbp.dhs.gov by midnight EST Monday, February 9, 2026. Be sure to include “Comments to CBP re: OMB Control Number 1651–0111” in the subject line of your email message.

Jan 14 2026

US wants direct access to police databases worldwide

The US government is seeking direct access to police databases in other countries, as a condition of inclusion in the US Visa Waiver Program (VWP). Citizens of countries in the VWP are allowed to enter the US for limited short visits under the without having to apply or pay for standard visas to the US. So inclusion in the VWP is a valuable incentive the US can use to pressure other countries to make other concessions to the US.

The US says that any country not agreeing to a so-called Enhanced Border Security Partnership (EBSP) giving the US government access to its domestic police database by the end of 2026 will be expelled from, or not admitted to, the VWP.

The first EBSP agreement was signed in September 2025 between the US and Bahrain. The European Union authorized EBSP negotiations with the US in December 2025, despite concerns raised in September 2025 in an opinion by the European Data Protection Supervisor. EBSP negotiations are ongoing between the US and other countries in the VWP.

There’s been almost no discussion in the US of the EBSP negotiations or agreements. None of these agreements have been submitted to the US Senate for ratification as treaties.

The most detailed reporting about EBSP has come from Europe and has been based on documents from European governments.  This presentation at the 39C3 conference earlier this month in Germany by Matthias Monroy gives a good overview of what’s known and the questions that remain.

Labeling these agreements “partnerships” implies reciprocity. But most criminal investigations in the US are carried out by state or local police and aren’t included in any national database. The NCIC database hosted by the FBI is an index to records of arrests, convictions, and court orders such as warrants, but doesn’t identify people who are being investigated but for whom no warrant has been issued. As a result, EBSP agrrements will give US authorities access to much more information about foreigners in countries with entralized police record-keeping than foreign governments will get about people in the US.

The announcement of the signing of the USA-Bahrain EBSP agreement says that it “facilitates the automated exchange of biometric data between Bahrain and DHS”. The EBSP agreements thus provide a self-justifying pretext for integration of the US government’s biometric databases, in order to make them available to foreign police.

US data will be made available not just to democratic foreign governments but to ones like Bahrain — a repressive regime in which the hereditary monarch rules by decree. The US says that data sharing pursuant to the EBSP will “safeguard both countries”, but Bahraini dissidents and asylum seekers probably won’t see it that way. Once data is disclosed by the US to foreign authorities, there’s no way for the US to control, or even to know, how or against whom it’s used, or with which other repressive regimes it’s shared.

Dec 10 2025

CBP wants all visitors to install and use its smartphone app

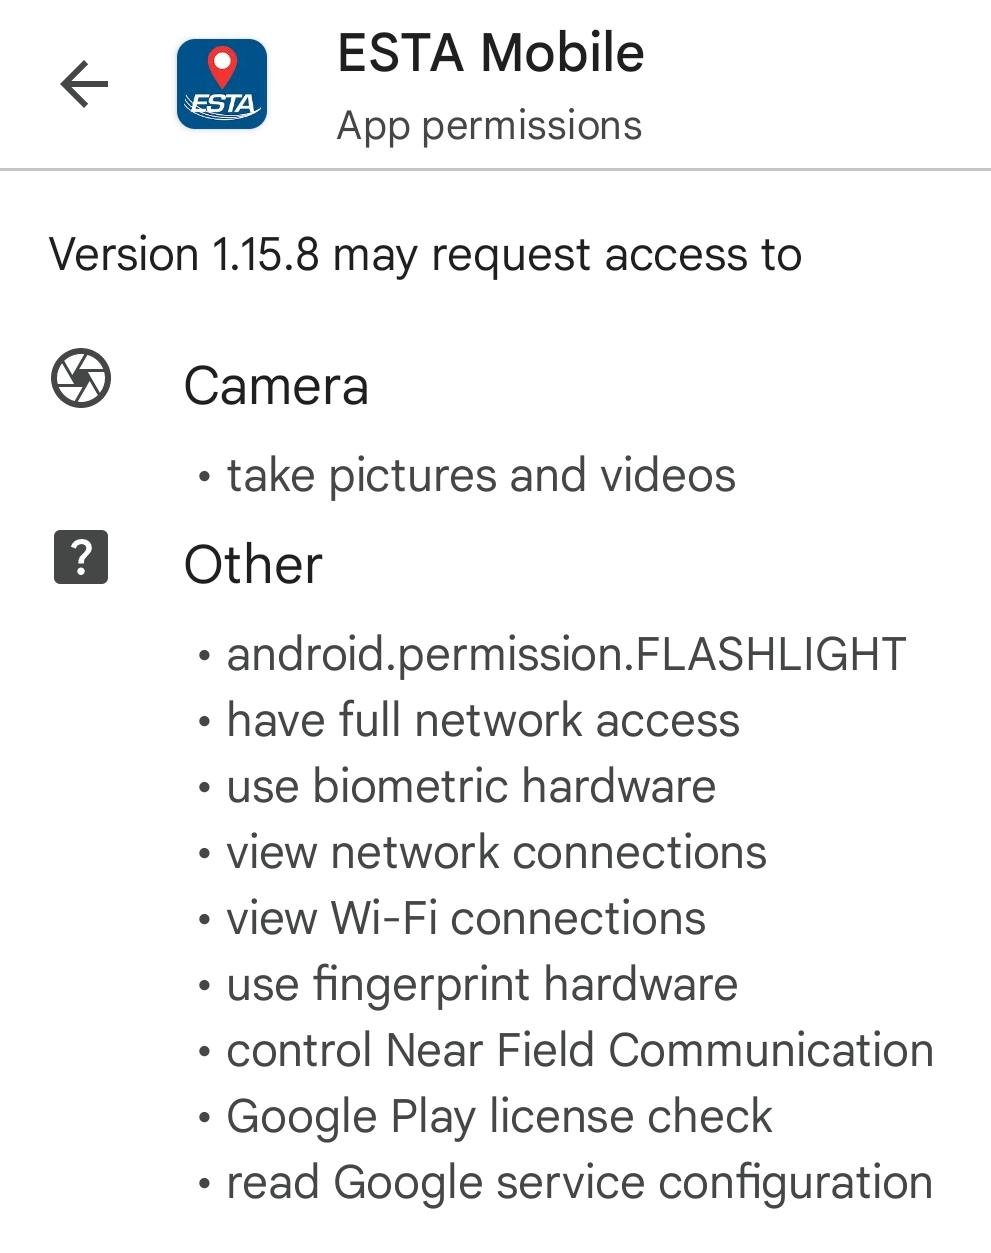
Permisisons requeste by ESTA Android app

[Permissions requested by ESTA Android app. Why does CBP want to be able control your flashlight?]

By a notice published today in the Federal Register, US Customs and Border Protection (CBP) is requesting approval not only to make all foreigners visiting the US without visas submit a comprehensive set of biometric identifiers (“face, fingerprint, DNA, and iris”) but to do so by installing and using a closed-source CBP smartphone app that requires permission to access Wi-Fi scanning and network data; take photos and video; access any fingerprint, iris scan, or other biometric sensors, and even turn on and off your flashlight.

Each visitor to the US under the Visa Waiver Program (VWP), for which the fee has recently been raised from $21 to $40 per person, would be required to submit, in advance, through this smartphone app, identifiers for all social media accounts they have used in the last five years.

Each visitor would also be required to submit what CBP calls “High Value Data Elements”. According to the notice:

The high value data fields include:

a. Telephone numbers used in the last five years;
b. Email addresses used in the last ten years;
c. IP addresses and metadata from electronically submitted photos;
d. Family member names (parents, spouse, siblings, children);
e. Family number telephone numbers used in the last five years;
f. Family member dates of birth;
g. Family member places of birth;
h. Family member residencies;
i. Biometrics—face, fingerprint, DNA, and iris;
j. Business telephone numbers used in the last five years;
k. Business email addresses used in the last ten years.

CBP thinks that the average visitor could compile and enter all of this data (typing on a smartphone) in 22 minutes,  including the time needed to contact each of their siblings and children to find out their five-year history of addresses and phone numbers.

Welcome to the 2026 World Cup!

Applicants for US visas are already required to provide a much more extensive set of personal data, including biometrics and identifiers for all social media accounts they have used. So this proposal, if approved, would expand collection of biometrics, social media identifiers, and the additional “high value data elements” to almost all foreign visitors to the US, with or without visas. The only remaining exception, which CBP doesn’t mention, is for asylum seekers who may have no documents and who require no pre-approval.

We continue to oppose warrantlesss, suspicionless compelled disclosure of social media or biometric identifiers or other information as unconstitutional and a violation of the human rights of travelers. And we oppose any requirement to provide this information in advance, when it could be collected on arrival in the US, when visitors apply for admission.

Read More →