Oct 17 2026

SFO “elected” to pay for DHS facial recognition system
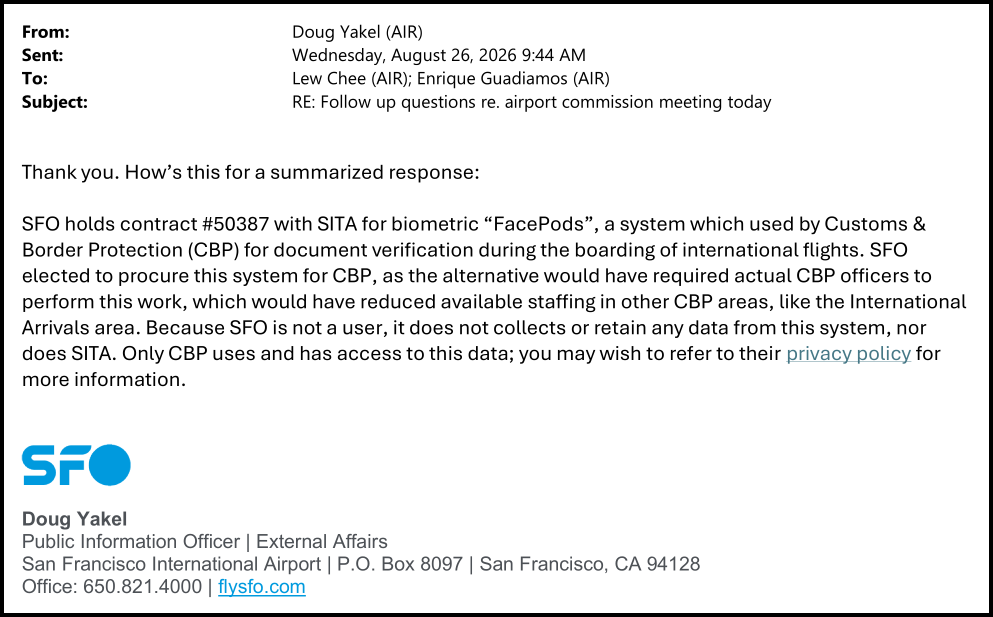
[Internal SFO email message released in response to our public records request. The claim that only CBP has access to the facial images is false. The official CBP notice for these records indicates that they are routinely shared with other DHS components, which include ICE, and with other US and foreign agencies.]

We’ll be back at the San Francisco Airport Commission on Tuesday, October 20th (9 a.m., S.F. City Hall, Room 400) to renew our demands for the airport to end its illegal funding of facial recognition infrastructure for immigration enforcement, review and publicly report on all of its contracts and collaboration with the US Department of Homeland Security (DHS), and post prominent signs warning travelers of the invisible risk that information in airline reservations, even for domestic flights, can be passed on to Immigration and Customs Enforcement (ICE) and used to target travelers for detention or deportation.

The last scheduled Airport Commission meeting was canceled. We’ve received no response to any of our specific requests for action by the Airport Commission.  In the meantime, though, we’ve received responses to some of our requests for airport records which confirm the illegality of some of the airport’s actions and the need for action.

Internal SFO email messages show that SFO officials illegally “elected” to pay for facial recognition cameras connected to to the DHS Traveler Verification Service, in order to spare US Customs and Border Protection officers from having to photograph departing international passengers and free up CBP officers to spend more time on other duties at the airport — duties which include assisting ICE officers with detentions of travelers and other immigration enforcement activities.

According to one internal SFO message summarizing information provided by airport operations managers:

SFO holds contract #50387 with SITA for biometric “FacePods”, a system which used by Customs & Border Protection (CBP) for document verification during the boarding of international flights. SFO elected to procure this system for CBP, as the alternative would have required actual CBP officers to perform this work, which would have reduced available staffing in other CBP areas.

Facial images taken by these city-funded cameras are transmitted over a city-funded connection to CBP. CBP shares them with other DHS components including ICE, and uses them to train the facial recognition algorithm used by ICE to determine who to detain or deport.

When this system was first tested, CBP officers staffed the cameras. But CBP has since tried to get airports to provide the cameras and and airlines to operate them. Airlines are incentivized to collaborate in this passenger surveillance and control scheme by being given free use of the TVS system (paid for, in this case, by SFO) for their own business process automation and commercial surveillance.

Pursuant to San Francisco’s Sanctuary City Ordinance, city and county agencies such as the airport may not “elect” (i.e choose) to provide or pay for services to support immigration enforcement. City funds may be spent on such services not as a voluntary choice but only to the extent required by Federal regulations.

Federal regulations (8 CFR §234.4) require each international airport to pay for some services and facilities for use by Federal immigration enforcement agencies, including “such temporary detention quarters as may be found necessary.”

SFO Airport Director Mike Nakornkhet and S.F. City Attorney David Chiu wrote to CBP earlier this month  to “express concern” about CBP’s treatment of detainees at SFO. But this focuses attention on precisely that aspect of immigration enforcement at SFO over which the city has the least control. This makes it easy for city officials to claim that their hands are tied — as they are, to some degree, with respect to the immigration jail at SFO.

But not everything Federal agencies ask the airport to provide is required by Federal regulations. The Airport Director, the City Attorney, and the Airport Commission should focus on the decisions within their control: voluntary financial support by SFO for facial recognition  infrastructure and services used for immigration enforcement, and signage to warn travelers about the invisible risks of airline-TSA-ICE data sharing.

No Federal regulation requires any airport to provide, or any airline to use, the TVS facial recognition system. The notice of CBP’s regulations for use of facial recognition for departing air travelers makes explicit that, “Participation in CBP’s biometric entry-exit program will remain voluntary for carriers under this final rule. If air carriers or airports do not participate, they will continue conducting manual identity verification.”

TVS is a choice for the airport — a choice that the Sanctuary City Ordinance prohibits SFO to make. Voluntary funding of immigration enforcement activities by any agency of the City and County of San Francisco, including the airport, is forbidden.

SFO’s contract #50387 with SITA is a voluntary payment for services that are used for immigration enforcement. As such, it is prohibited by the S.F. Sanctuary City Ordinance. It is the legal duty of the S.F. Airport Commission to terminate this contract immediately. We reiterate our demand that the Airport Commission place the termination of contract #50387 on its agenda for action at its next meeting.
Read More →

Sep 14 2026

Court bars AAMVA from giving away driver’s license data — for now

Last Thursday, September 10th, Judge Anthony Trenga of the U.S. District Court for the Eastern District of Virginia heard arguments on whether his temporary restraining order (TRO) barring the bulk transfer of commercial driver’s license records from the American Association of Motor Vehicle Administrators (AAMVA) to the U.S. Deopartment of Transportation (DOT) should be converted into a preliminary injunction.

If granted by the court, a preliminary injunction would remain in effect until a final ruling in the lawsuit brought by state governments challenging the data demand by the Feds.

Judge Trenga took the motion for a preliminary injunction under advisement without issuing a decision.

In response to the motion for a preliminary injunction, DOT cooked up an array of patently pretextual and impermissibly ex post facto new excuses for why it needs a dump of all the records of commercial driver’s licenses in AAMVA’s SPEXS database.

DOT also made a new threat to have its Office of Inspector General demand the data, in bulk, without a warrant or probable cause, for investigation of unspecified possible crimes.

It seems unlikely that either the briefs or the oral argument last Thursday have given Judge Trenga any reason to depart from the reasoning in his initial decision granting a TRO.

In that ruling, Judge Trenga found multiple independent ways in which the demand for this data is illegal. He also found that the claimed basis for the demand is a pretext to obtain data that would actually be used (illegally) for immigration enforcement:

The FMCSA has also conceded it has not demanded the MPRs [Master Pointer Records] solely to use those records itself, but also to share them with DHS for “immigration enforcement purpose[s].”… But the relied upon exception under the DPP A that authorizes disclosure of protected data to effectuate FMCSA’s own statutory mandate does not authorize FMCSA to simply pass that data onto another agency….

[W]hen repeatedly pressed at the hearing on this point, the Federal Defendants were unable to explain how the data would in fact assist them in performing their statutory functions, or point to anything that they cannot already do without this data…

Federal Defendants have failed to dispel the compelling inference that they seek these 17 million files in large part, if not primarily, for immigration enforcement, which is not part of [FMCSA]’s statutory mandate….

[B]ecause the Data Demand is unlawful, the public interest inherently favors issuing an injunction….

The issuance of an injunction is also in the public interest given the harm the termination of federal funding to AAMVA would cause since CDLIS would effectively cease its operations and impair Plaintiff States’ ability to issue and renew CDLs and compromise the safe operation of commercial motor vehicles…. Furthermore, as the AAMVA contends, the “CDLIS … is interconnected with all forms of driver licensing” and therefore any shutdown “could disrupt, or even stop, the issuance and renewal of any driver license in the United States.”

Meanwhile, the American Federation of Teachers (AFT) has moved to intervene in the case on behalf of AFT members including school bus drivers whose commercial driver’s license data is included in the Federal data demand.

AFT says that states — like AAMVA — have their own interests, including retaining Federal funding, and can’t be relied on to represent the interests of individuals whose data is at risk. AFT’s motion to join the case against both DOT and AAMVA is set for a hearing this Wednesday, September 16th.

While Judge Trenga has ordered AAMVA, for now, not to hand over records of all commercial driver’s licenses to DOT, the outcome of the lawsuit remain uncertain.

No one state such as California can control AAMVA’s decisions. The head of each state’s driver licensing agency has one vote on AAMVA’s board of directors, so states that want to hand over AAMVA’s records for immigration enforcement can outvote those that don’t.

The ongoing litigation should teach a lesson to California and other states that once they hand over data to AAMVA, they can’t control to whom or for what purposes it is passed on voluntarily or involuntarily by AAMVA to Federal agencies or other third parties.

The same lesson applies to non-commercial as to commercial driver’s licenses, both of which are stored by AAMVA in the same database. In  comments to Wendy Fry and Khari Johnson of Cal Matters, a spokesperson for California Governor Gavin Newsom falsely claimed that AAMVA’s databases of commercial and non-commercial driver’s license records “are separate systems”. In fact, CDLIS records for commercial driver’s licenses and S2S records for non-commercial licenses are both stored by AAMVA in the same SPEXS database.

Californians should have second thoughts about the upload of non-commercial driver’s license records to SPEXS, planned for 2027 and authorized by a law rushed through the state legislature by Governor Newsom while Federal demands for SPEXS data were already pending.

Sep 01 2026

9th Circuit upholds injunction against cash transaction reporting order

In March 2025 we reported on an order from the Financial Crimes Enforcement Network (FinCEN) of the US Department of the Treasury commanding all money transfer agencies and currency exchanges in seven counties in California and Texas along the US-Mexico border to file reports with FinCEN including the identities of all customers engaging in all cash transactions over $200.

Separate lawsuits challenging this order were brought by the Institute for Justice on behalf of storefront financial services business in California and Texas.

FinCen revised and reissued the order several times, raising the reporting threshold from $200 to $1000 and changing the areas to which the order applied. But despite these moves by FinCEN, US District Courts in both California and Texas issued preliminary injunctions against enforcement of the order.

A year later, a panel of the 9th Circuit Court of Appeals has upheld the injunction in the California case by a 2-1 vote.

Read More →

Aug 31 2026

Airline reservations are still being used to target dissidents

Much of the public interest in the case of Samuel Tunick has focused on the charge — carrying up to a five-tear prision sentence — that  Mr. Tunick “destroyed property to prevent its seizure” by the government by giving Customs and Border Patrol (CBP) agents at the Atlanta airport a “duress password” for a smartphone Mr. Tunich was carrying when he returned from an international trip.

The phone seized from Mr. Tunick at the airport was running Graphene OS, an open-source variant of the Android operating system. When one of the CBP agents entered the password Mr. Tunick (under duress) provided, it wiped the phone’s user memory and reset the phone to a state as though the OS had just been installed.

The option to set a “duress password” that wipes the phone, in addition to one or more user passwords for separate user spaces, is a feature of Graphene OS intended to reduce the risk of coerced disclosure of data.

Mr. Tunick was arrested at the airport last December, but briefing on pre-trial motions is ongoing and no trial date is in sight.

This is an important test case on the issues raised by the “duress password”, the way it functions in Graphene OS, and compelled disclosure of passwords generally.

But there’s another concerning issue raised by the facts in this case: How airline reservations were used to target Mr. Tunick, in advance, for special treatment on arrival including seizure of his phone and pressure to disclose a password for the phone.

Mr. Tunick wasn’t singled out for “secondary screening” at random or because of anything he said or did or was carrying that appeared “suspicious” to CBP agents at the airport.

According to a report of a motion hearing in July, the transcript of which has not yet been released, CBP agents were sent an automatically generated email message before his flight got to Atlanta, alerting them in advance that a person in whom they had previously indicated an interest had reservations on a specific airline, flight number, date, and time.

Read More →

Aug 30 2026

SFO evades criticism of its role in immigration enforcement

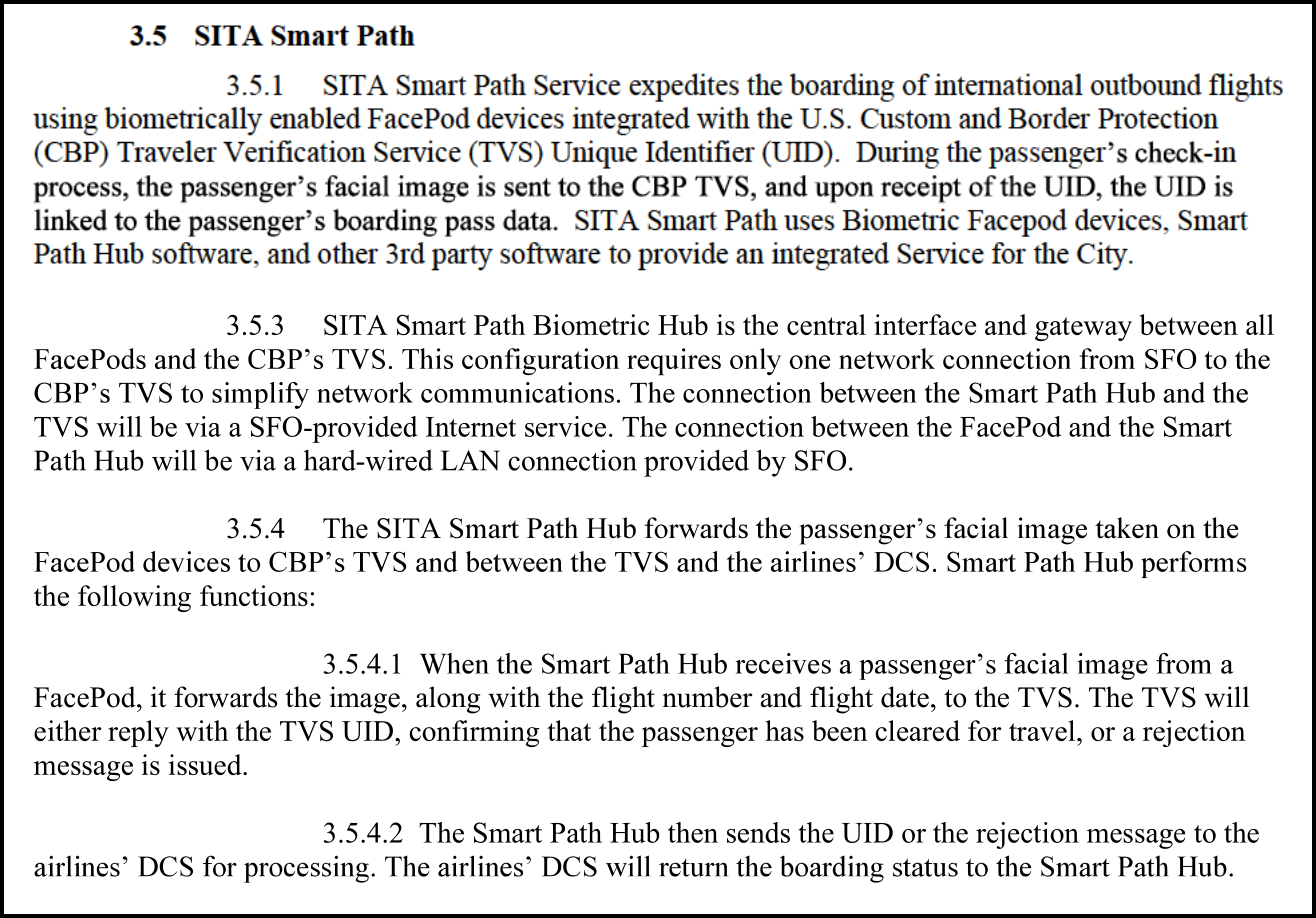
[Excerpt from illegal contract awarded by SFO to SITA in violation of the S.F. Sanctuary City Ordinance describes facial recognition hardware, software, and services paid for by the City and County of San Francisco, deployed by SITA on City and County property at SFO, and used to collect and transit mug shots of passengers and “permission to board” messages between airlines, the airport, and CBP/DHS, for purposes including immigration enforcement.]

At the San Francisco Airport Commission meeting on August 15th, a dozen members of the public (video, Mission Local, SF Public Press) called on the Airport Commission to comply with San Francisco’s “Sanctuary City” ordinance, which prohibits use of S.F. City and County resources — including airport property and funds — for immigration enforcement.

Another 35 people sent written comments to the Airport Commission on the same subject.

Many of the commenters, who included including supporters of Indivisible SF, Bay Resistance, and the Identity Project, among others, explicitly endorsed the comments of the Identity Project and our specific requests for action by the Airport Commission.

The Airport Commissioners neither discussed nor responded to any of our criticism. But the Director of SFO, Mike Nakornket, opened the meeting by trying to preemptively deflect our criticism with a mix of false, untested, inadequate, and unresponsive claims about the city’s actions and legal authority as the owner, landlord, and operator of the airport.

False: Airport Director Nakornket  claimed that, “SFO is not involved in the sharing of passenger information for immigration enforcement  purposes, which we understand occurs on a federal level between DHS agencies.”

But the Airport Director should know that this isn’t true.

Read More →

Aug 14 2026

DHS demands AAMVA’s national commercial driver database


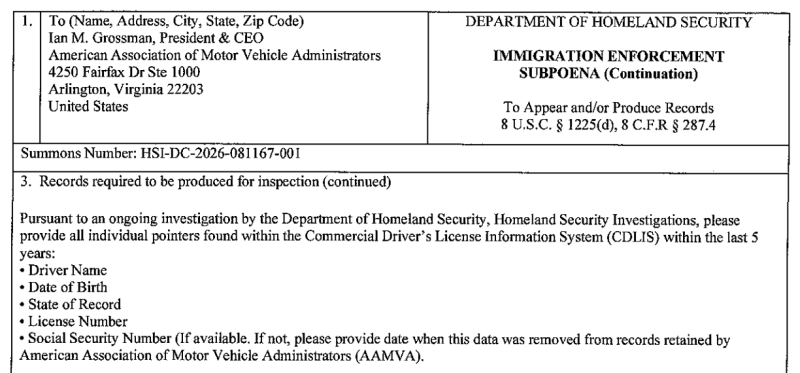
The US Department of Homeland Security (DHS) has subpoenaed the American Association of Motor Vehicle Administrators (AAMVA) for a copy of all entries in the CDLIS national database of state-issued commercial driver’s licenses held by AAMVA. The administrative subpoena was issued August 11th and ordered AAMVA to hand over a copy of all records that were found in the CDLIS database any time in the last five years, by 8 am Monday, August 17th.

DOT says that “AAMVA operates the CDLIS database on behalf of the federal government; it is contractually and legally obligated to furnish the requested records at FMCSA’s direction.”

In response, a group of states led by Illinois has filed separate lawsuits in Virginia, where AAMVA is incorporated, against the DHS to quash the subpoena and against AAMVA and the US Department of Transportation (DOT) to enjoin AAMVA from complying with the DOT’s parallel demand for the same data.

US District Judge Anthony Trenga immediately issued temporary stays which prohibit AAMVA from complying with the subpoena and prohibit any actions by DOT to punish AAMVA for noncompliance with the DHS subpoena or DOT demand for CDLIS data. Initial hearings before Judge Trenga in both cases are scheduled for Thursday, August 20th.

We hate to have to say, “We told you so.” But in this case, we told you so.

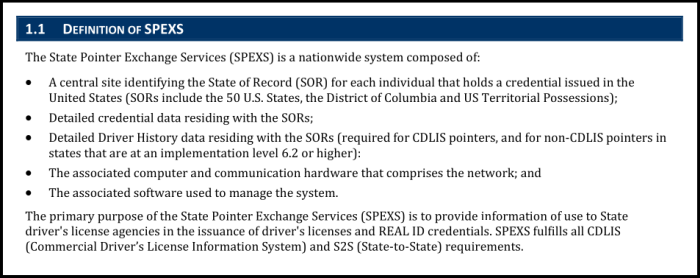
The CDLIS database is the little brother for commercial driver’s licenses (for truckers) to the big brother SPEXS database for all driver’s licenses and state-issued ID cards. Like SPEXS, CDLIS is a national database of “pointer” records (including name, date of birth, state, license or ID number, and Social Security Number)  aggregated from information uploaded by state motor vehicle agencies but held by AAMVA or AAMVA’s contractors.

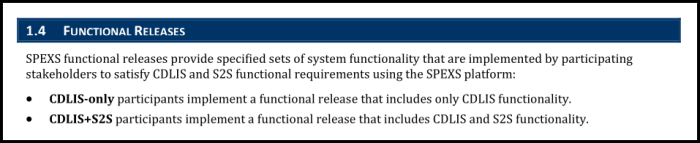
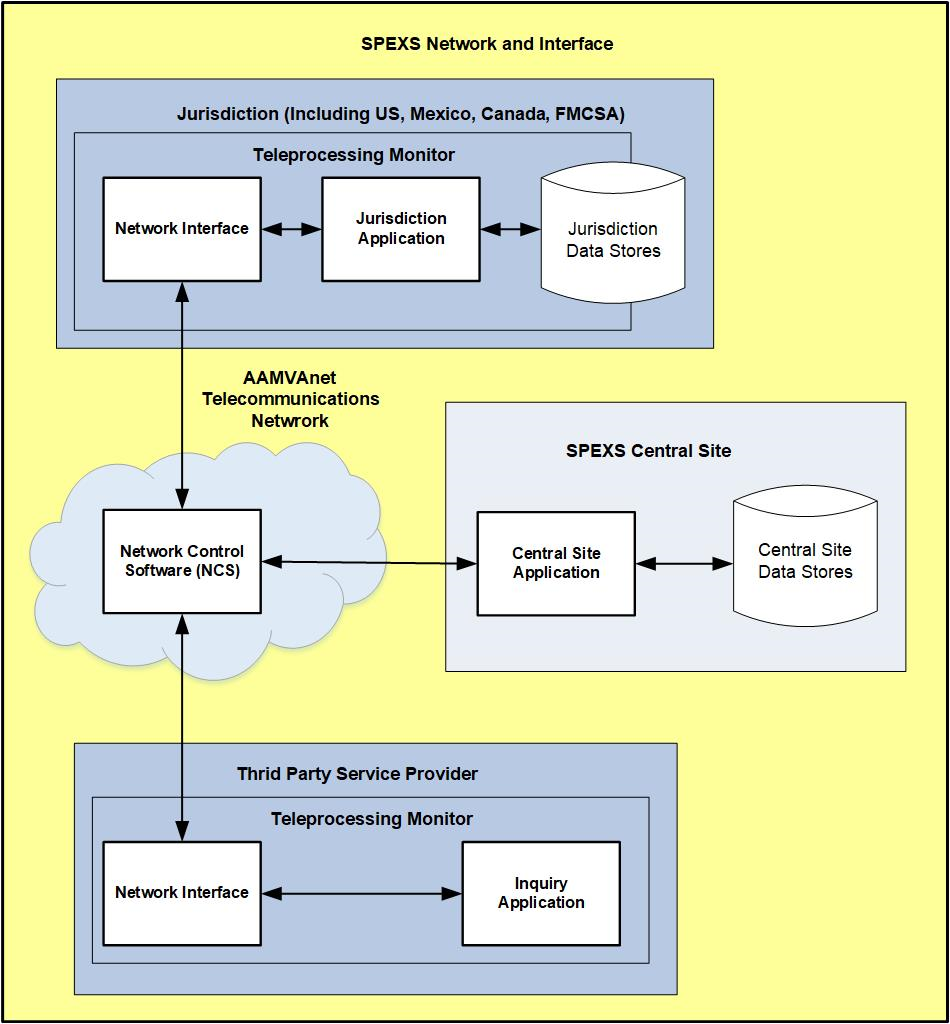
CDLIS (commercial license) and S2S (non-commercial license) pointer records are all stored in the same SPEXS database as part of AAMVA’s central site:

[Excerpts from AAMVA’s “SPEXS System Specification”]

We’ve warned repeatedly that once data is uploaded to AAMVA’s SPEXS database, Federal agencies could demand it from AAMVA in bulk. State authorities, most recently in California, have brushed off our warnings. But as conceded in declarations from the California Department of Motor Vehicles in one of the new cases, the California DMV has already been uploading CDLIS information about commercial driver’s licenses to SPEXS, and plans to start uploading “S2S” data about all California license to SPEXS in 2027.

The DHS is now seeking to obtain driver’s license data from every state, in bulk, through an administrative subpoena to AAMVA, for use for immigration enforcement, in exactly the manner and for the purpose we predicted and warned about.

AAMVA’s role is noteworthy and contemptible, although unsurprising.

AAMVA was sent a demand for the entirety of the CDLIS database on June 25th, but didn’t tell the states that had uploaded the data  in question about the Federal demand until almost a month later on July 23rd. State can’t count on prompt notice from AAMVA.

Even now, AAMVA isn’t  challenging the demand for CDLIS data. AAMVA is a defendant, along with the Federal agencies, in the lawsuits brought by states to protect their residents’ data against bulk disclosure to Federal agencies for immigration enforcement.

According to the complaints, the DHS and DOT have threatened to cut off all Federal funding for AAMVA, including funding for CDLIS itself (and presumably also SPEXS), if AAMVA doesn’t hand over the requested data. AAMVA depends on Federal funding, so it can’t afford to challenge Federal demands, making it in effect a captive proxy for the Feds despite being a nominally non-governmental private nonprofit corporation.

Presumably, the Feds will learn from AAMVA’s failure to challenge their demands for the data it holds. Next time, they’ll come back with a subpoena that includes a gag order prohibiting AAMVA from disclosing the subpoena to states that uploaded the data, so states will have no chance to file lawsuits like the ones filed this week.

The obvious next step after that would be a similar demand for SPEXS data about ordinary non-commercial licenses, probably as soon as California completes its planned bulk upload to SPEXS sometime early in 2027.

Officials in California and other states can no longer claim this isn’t possible.

State legislators need to act, now, to withdraw their states from SPEXS, before the DHS expands its data demands from the commercial licenses in CDLIS to all licenses in SPEXS.

Jul 31 2026

“Can SFO rein in the feds?”

As discussed in a feature article today by Clara-Sophia Daly on Mission Local, recent searches and arrests of passengers trying to board domestic flights at San Francisco International Airport (SFO) have prompted us to question what the airport has done, and what more it could and should do, to comply with city ordinances regulating use of surveillance technology and restricting collaboration with immigration enforcement.

The arrest of Iryna Gorb by ICE at SFO on July 22nd and the search of Nikolas De Bremaeker by the TSA (and/or by Covenant Aviation Security, the contractor that supplies most of the checkpoint staff at SFO) at SFO on June 10th, raise questions about (1) the technologies in use to flag passengers to components of the Department of Homeland Security (DHS) based on airline reservations, (2) whether equipment owned or operated by the airport is used to collect data passed on the DHS, (3) what, if any, limits are placed on warrantless access by DHS agents to airport premises, and (4) whether the policies of the airport, as put in place by the SF Airport Commission as an agency of the City and County, comply with city ordinances.

For both domestic and international flights, the DHS requires airlines to send information about all passengers and their itineraries to DHS components starting 72 hours before departure.  Reservation and itinerary information for international flights is sent to US Customs and Border Protection (CBP) and included in its Automated Targeting System (ATS). Information for domestic flights is sent to the Transportation Security Administration (TSA) through its Secure Flight system.

No airline is allowed to issue a boarding pass for either a domestic or international flight unless and until it receives an individualized, per-passenger, per-flight permission message from the TSA or CBP in the form of a “boarding pass printing result” (BPPR). The default in the absence of a favorable BPPR is not to allow them to fly. These fly/no-fly decisions are based on a black box of secret algorithms that incorporate list-based rules (blocklists) and other rules based on other known and unknown data.

Once such a data collection and  algorithmic control mechanism is in place, it’s easy to add lists or other rules to the algorithm or add recipients to the data stream.

What’s less well known is that the DHS doesn’t just use the information it gets from airlines to decide whether or not to allow you to fly. It can also use this information to generate “handling codes” instructing checkpoint staff to conduct special searches of your person and property, or to generate messages to other agencies that may want to arrange an “unwelcoming” party to intercept you at the airport, on departure or on arrival, to question, search, or arrest you – with or without a warrant.

We question the legality of many of these activities. Many of them have not yet been reviewed or approved by any court, and have little or no basis in law.

Airline passengers need to know that, legal or not, this is happening.

Travelers also need to know that, as we were the first to report last year (see here and here) and as was later confirmed by the New York Times and American Oversight, some of the most intrusive and legally questionable aspects of these systems of surveillance and control of air travel, based on reservation data from airlines, have in the last year been expanded from international flights to domestic flights. Air travelers should beware.

Read More →

Jul 16 2026

Gov. Newsom signs law to upload California data to national ID database

Ignoring objections from grassroots organizations from diverse communities throughout the state and a litany of lies to the legislature from the California Department of Motor Vehicles (DMV), Gov. Gavin Newson signed a bill into law this week which authorizes the DMV to upload information about about all California driver’s licenses and state-issued non-driver ID cards to the SPEXS national ID database. The bill, SB-169, is effective immediately.

Gov. Newsom and the DMV have made much of the “guardrails” included in the bill. But as we testified at the last hearing before this bill was enacted (see video starting at 2:48:22) once the DMV uploads information about all California driver’s licenses and IDs to AAMVA (which holds the SPEXS database), the “guardrails” in this bill would do nothing to protect Californians against the threat that Federal or other states’ law enforcement agencies could obtain an order (1) requiring AAMVA to hand over this data in bulk and (2) prohibiting AAMVA from disclosing that order to the DMV or to the Californians — especially vulnerable immigrant and transgender Californians — against whom this data will be weaponized. Neither the DMV nor impacted Californians will even know this has happened, and it won’t be detectable by the audit of DMV records (not AAMVA records) required by SB-169.

In its report on the signing of SB-169, the Sacramento Bee erroneously states (perhaps based on misinformation from the DMV and/or the Governor’s office) that the data sharing authorized by SB-169 is “required by federal law.” But the regulations cited by the Bee apply only to those states that choose to comply with the REAL-ID Act.

As a coalition of 170 organizations said in a joint statement quoted by the Bee:

The first rule of combating tyranny is do not comply in advance. It is imperative that California not willingly give away data that the federal government could turn around and use to harm our communities.

No state is required to comply with the REAL-ID Act. No state is required to upload data about its residents to a database held by a private company, AAMVA.

This is a choice — the wrong choice — for Californians.

Jul 01 2026

Did California’s DMV Director lie to the legislature?

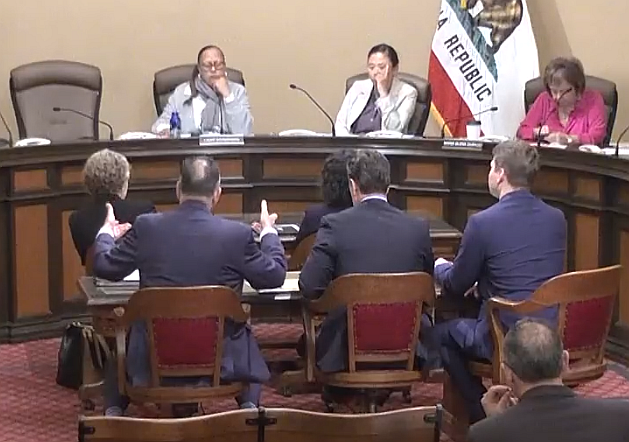
California DMV Director Steve Gordon with other DMV staff at witness table facing members and staff of Senate Budget Subcommittee #5

California DMV Director Steve Gordon responds to questions from members of Senate Budget Subcommittee #5 on Transportation, March 19, 2026

As part of their lobbying of the California legislature to change state law and appropriate $55 million to upload information about all California driver’s licenses and ID state-issued non-driver ID cards to the privately-held SPEXS national ID database, the Department of Motor Vehicles (DMV) and the office of Governor Gavin Newsom have claimed that the state is already “committed” to the planned upload, despite the fact that it would violate current state law restricting disclosure of license and ID records.

The latest responses to our public records requests show that this claim is false.

At a hearing on March 19, 2026, before Senate Budget Subcommittee $5 on Transportation, DMV Director Steve Gordon  testified (see video beginning at 1:42:00):

As I mentioned, you know, California has signed an agreement back in 2028 to effectuate, you know, the REAL ID Act and make sure that in fact, that we’re compliant, including State-to-State. So the agreement we have with the Department of Homeland Security, as well as the Transportation Security Administration, is we have a agreed upon date, which is the February [2027] date that you mentioned.

If the DMV Director, the Governor, or some other state official signed such an agreement purporting to commit the state to take actions prohibited by current state law, that raises important questions as to whether they violated their duty to comply with state laws, or whether they took it upon themselves to commit the legislature to change those laws.

After subsequent meetings in which the DMV and the Governor’s office doubled down on their claim that the state is already bound by signed “agreements” with the DHS and TSA, we filed public records requests with the DMV and the Governor’s office to find out who signed those agreements, when, and what the agreements say.

The response from the DMV and the Governor’s office was that they could find no record of any such agreements.

In our public records request, we cited DMV Director Gordon’s testimony and asked for:

…a copy of each agreement referred to by Director Gordon in this testimony, including the names, titles, and organizational or agency affiliations of each of the persons signing the agreement…. This request includes… the agreement(s) signed in 2018 and the agreement(s) that the state of California and/or the DMV currently has with the U.S. Department of Homeland Security and/or Transportation Security Administration regarding the “State-To-State” system, the date of participation by the state of California and/or the DMV in that system, or the February 2027 date referred to by Director
Gordon.

The Office of the Governor told us that it “has no records responsive to your request.” The DMV, after three weeks of delay, told us that it could find no contracts or agreements at all with the TSA, and that the only contracts or agreements with the DHS that it could find were a series of annual contracts for the DMV to pay the DHS per-query fees to use the DHS/USCIS Systematic Alien Verification for Entitlements (SAVE) system to check the citizenship and immigration status of applicants for California driver’s licenses and IDs. The DMV could find no contracts or agreements with the DHS related to the “State-to-State” system.

Assuming these responses to our request for public records to be accurate, there is no agreement form 2018 or more recently with the DHS or TSA committing California to participate in the S2S network or upload any information to the SPEXS database at AAMVA’s central site for S2S, much less any agreement committing the state ot a February 2027 “deadline” for this upload — contrary to DMV Director Gordon’s testimony.

This isn’t a new question or the first time that DMV Director Gordon appears to have lied about REAL-ID Act requirements. In our testimony as the only public witness at a state budget hearing in 2019, we pointed out (see video beginning at 1:10:23) that that the DMV was already making plans that would require this upload, but hadn’t sought funding or authorization from the legislature for it. We also raised many of the other issues that have re-emerged this year when the DMV belatedly sought approval and funding for the upload.

Following that 2019 hearing, DMV Director Gordon admitted to us that he had personally flown without ID and knew that no ID at all is required to fly, despite his personal appearances in DMV videos and “public service announcements” claiming that ID was required and that REAL-ID would be required to fly.

Neither California legislators nor the public should trust the DMV on this issue, especially when the DMV’s Director makes specific claims in official testimony — naming specific parties, dates, and details — of which the DMV can find no record.

As we said at this Monday’s hearing before the full Senate Budget Committee (see video starting at 2:48:22) once the DMV uploads information about all California driver’s licenses and IDs to AAMVA (which holds the SPEXS database), the “guardrails” in this bill would do nothing to protect Californians against the threat that Federal or other states’ law enforcement agencies could obtain an order (1) requiring AAMVA to hand over this data in bulk and (2) prohibiting AAMVA from disclosing that order to the DMV or to the Californians — especially vulnerable immigrant and transgender Californians — against whom this data will be weaponized.

This is a major policy question that shouldn’t be be bundled into the budget. There’s no urgency and no legal deadline — only a date picked by AAMVA for AAMVA’s convenience. There’s no reason not to remove this proposal form this year’s budget and budget trailer bill so that  it can be given full and deliberate consideration by the appropriate policy committees of the legislature.

There’s an alternative: As we’ve been telling the DMV and the legislature for years, instread of premature capitulation to DHS threats, California should be  working through its Attorney General to prepare to defend Californians against any attempt by the DHS and/or TSA to carry out their lawless threats to interfere with state residents’ right to travel if the state chooses not to comply with the REAL-ID Act.

Jun 27 2026

California legislature agrees to upload driver’s licenses to national database

Withdrawing its opposition under behind-the-scenes pressure from Gov. Gavin Newsom and lawless threats from the US Department of Homeland Security (DHS), the California legislature has agreed to fund and revise state law to authorize the upload of information about all driver’s licenses and ID cards issued by the state to the private SPEXS national ID database operated by the American Association of Motor Vehicle Administrators (AAMVA).

The budget compromise between Gov. Newsom and the legislature announced last night includes “guardrails” intended to give an illusion of protection for license and ID data.

There’s no time before the hearing on the budget compromise scheduled for Monday morning in the Senate Budget Committee for legislators to assess whether those guardrails will be effective. But to anyone aware of the real threat, it’s apparent that they are a sham.

That was inevitable, as we’ve pointed out in our previous statements to the legislature.

Once this data is transferred to AAMVA, components of the DHS or other Federal or state law enforcement agencies will be able to obtain it from AAMVA by court order. Such a subpoena or warrant could, and probably would, include a gag order prohibiting AAMVA from disclosing it to the state of California or to the individuals whose data is disclosed.

Even after the fact, neither California nor individual Californians will know that this has happened or be able to challenge it.

That data could be misused in many ways, but it’s especially likely be weaponized against  immigrant and transgende Californians who are already being targeted by Federal agencies and other states.

The summary of the proposed transportation budget trailer bill (AB 169) released last night says that it “Limits data sharing to only that required by federal law.” But that’s not true. “Compliance” with the REAL-ID by California or any other state is optional, not required. Neither the Federal REAL-ID Act nor any other Federal law requires, or could require, California or any other state to share any data with AAMVA, a private nonprofit corporation.

As we pointed out in our earlier testimony on the budget proposal,  California has a choice. The state could and should say “No” to premature capitulation to DHS threats.

The Legislature should reject this “compromise” sell-out. Instead, the state, through its Attorney General, could and should prepare to defend Californians against any interference by the DHS or Transportation Security Administration (TSA) with our right to travel.